In 2010 a Zeus module that hid a VNC session on the victim’s machine cost $10,000. In December 2022 PureCoder sold one for $99 a year. The trick got cheap, the product that kept being maintained got expensive again, and I couldn’t find a public write-up of how this one actually does it.
Context
You will notice I am no longer posting decompilations of live binaries. These blog posts serve as the precursor rationale for the private technical twin analysis.
1. Second on the board
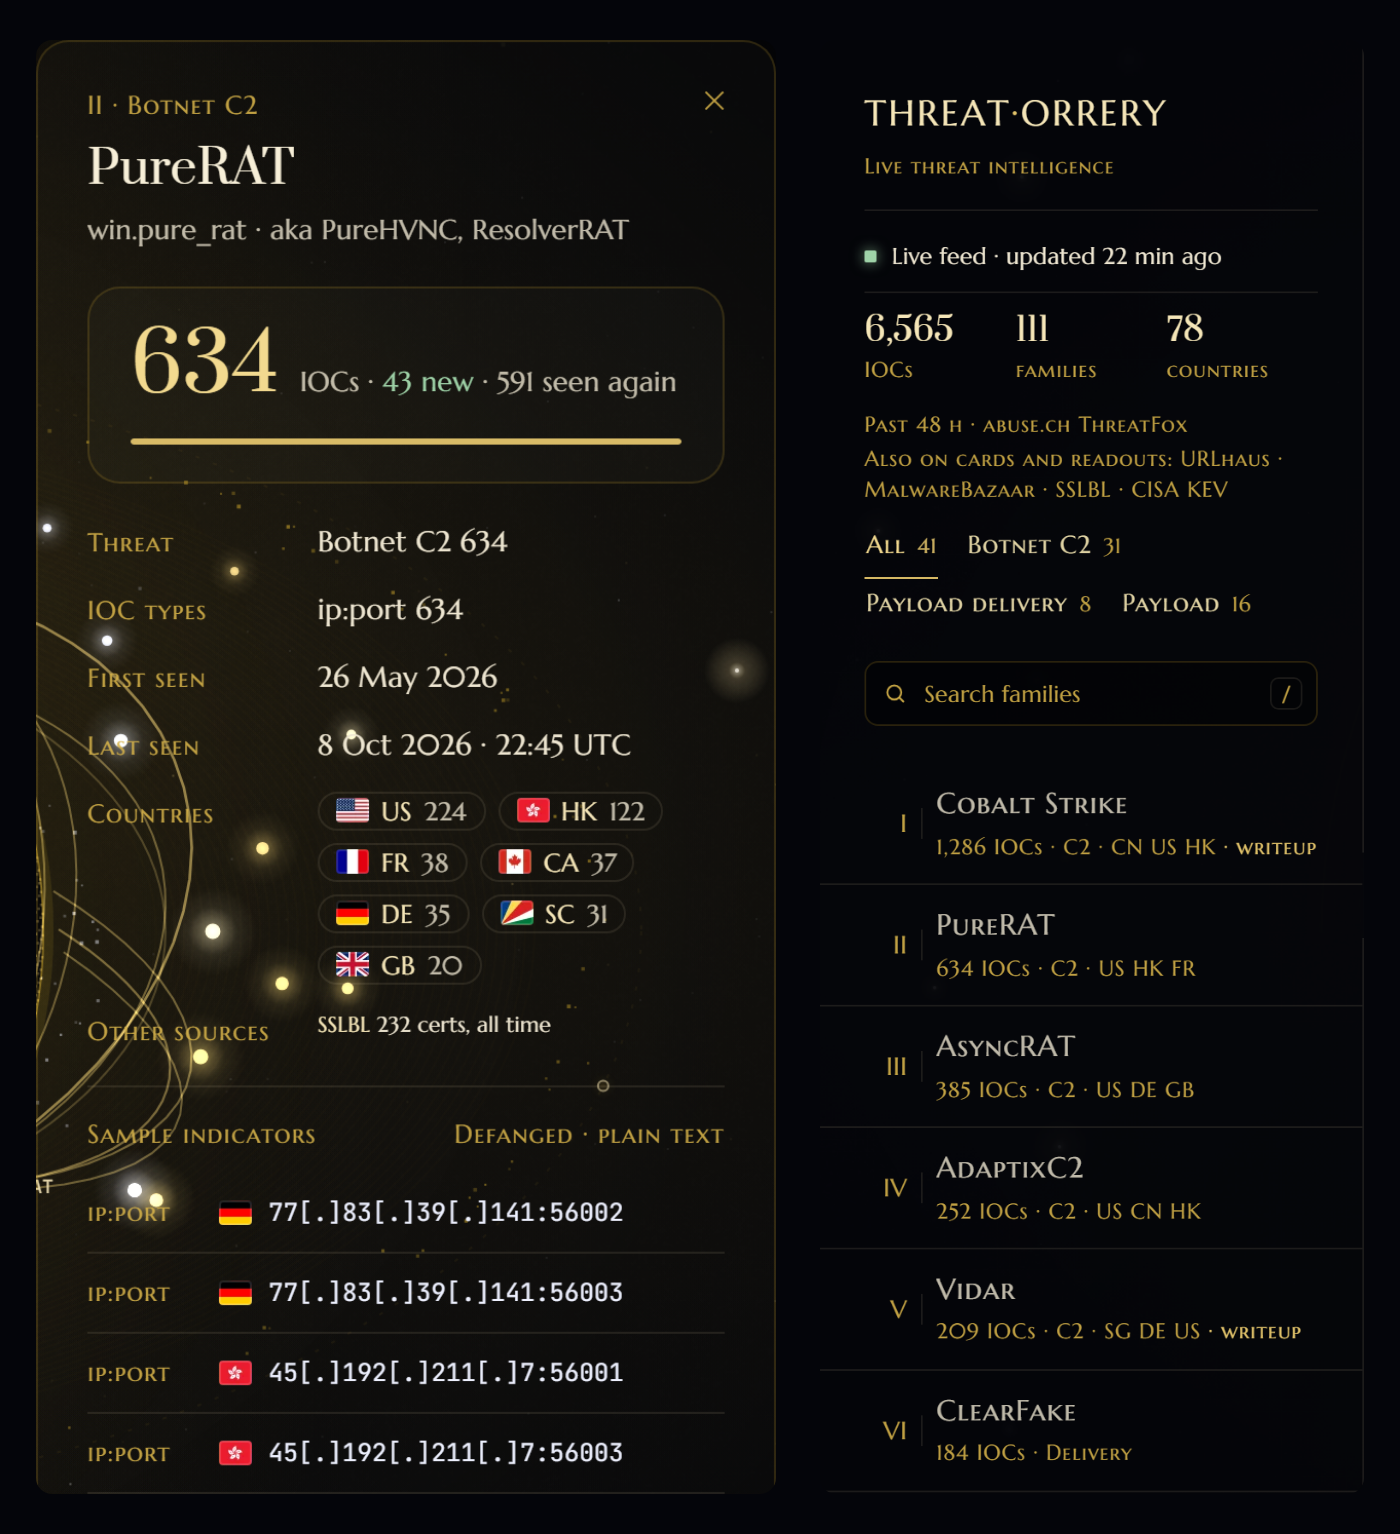
On 8 October 2026 PureRAT had more indicators in this site’s Threat orrery than any other named family except Cobalt Strike: 634 in 48 hours, every one a bare IP and port, every one command and control, mostly in the US and Hong Kong. AsyncRAT, the RAT everyone compares it to, had 385. The feed lists PureRAT with two aliases, PureHVNC and ResolverRAT. That’s three names for one family, sold by one seller, and a good share of what’s written about it is an argument over which name to use.
Context
PureRAT is a remote access trojan: an implant that gives an operator a live session on the victim’s machine. Its seller, who goes by PureCoder, also sells a crypter that packs it, a stealer, a miner, a clipper and a botnet loader. This post keeps coming back to one feature, the hidden desktop (hVNC): a second Windows desktop the user never sees, where the operator drives the victim’s own browser. PureHVNC was the product that sold it. PureRAT took over its features.
This post is built from public reporting and my own earlier work. It has no new sample analysis. It covers who PureCoder is, how the suite fits together, what the RAT does on the wire, whether it’s AsyncRAT in a new coat, what its hidden desktop shares with TinyNuke (and why nobody can say), why hidden desktops got so cheap, and what a defender can see. Where something is mine and not a public report, I say so. Two things about the early days don’t appear in any public report I found: a private sale of the first PureHVNC, which I can date from my own work, and a link between PureMiner and the seller’s start-up money, which I can’t. I come back to both.
2. PureCoder: one handle, a whole shop
PureCoder is a seller, not a campaign. The earliest public anchor is PureCrypter, on sale from at least March 2021 at an author-run Sellix store. Zscaler read the store in June 2022, Menlo read it again in February 2023, and ANY.RUN found the seller’s old site dating distribution to March 2021. Nothing public goes back further. On HackForums the account is marked as a vendor since 2021 too (my evidence). In September 2025 Check Point said little to nothing had been known about the developer’s time zone or country before its report.
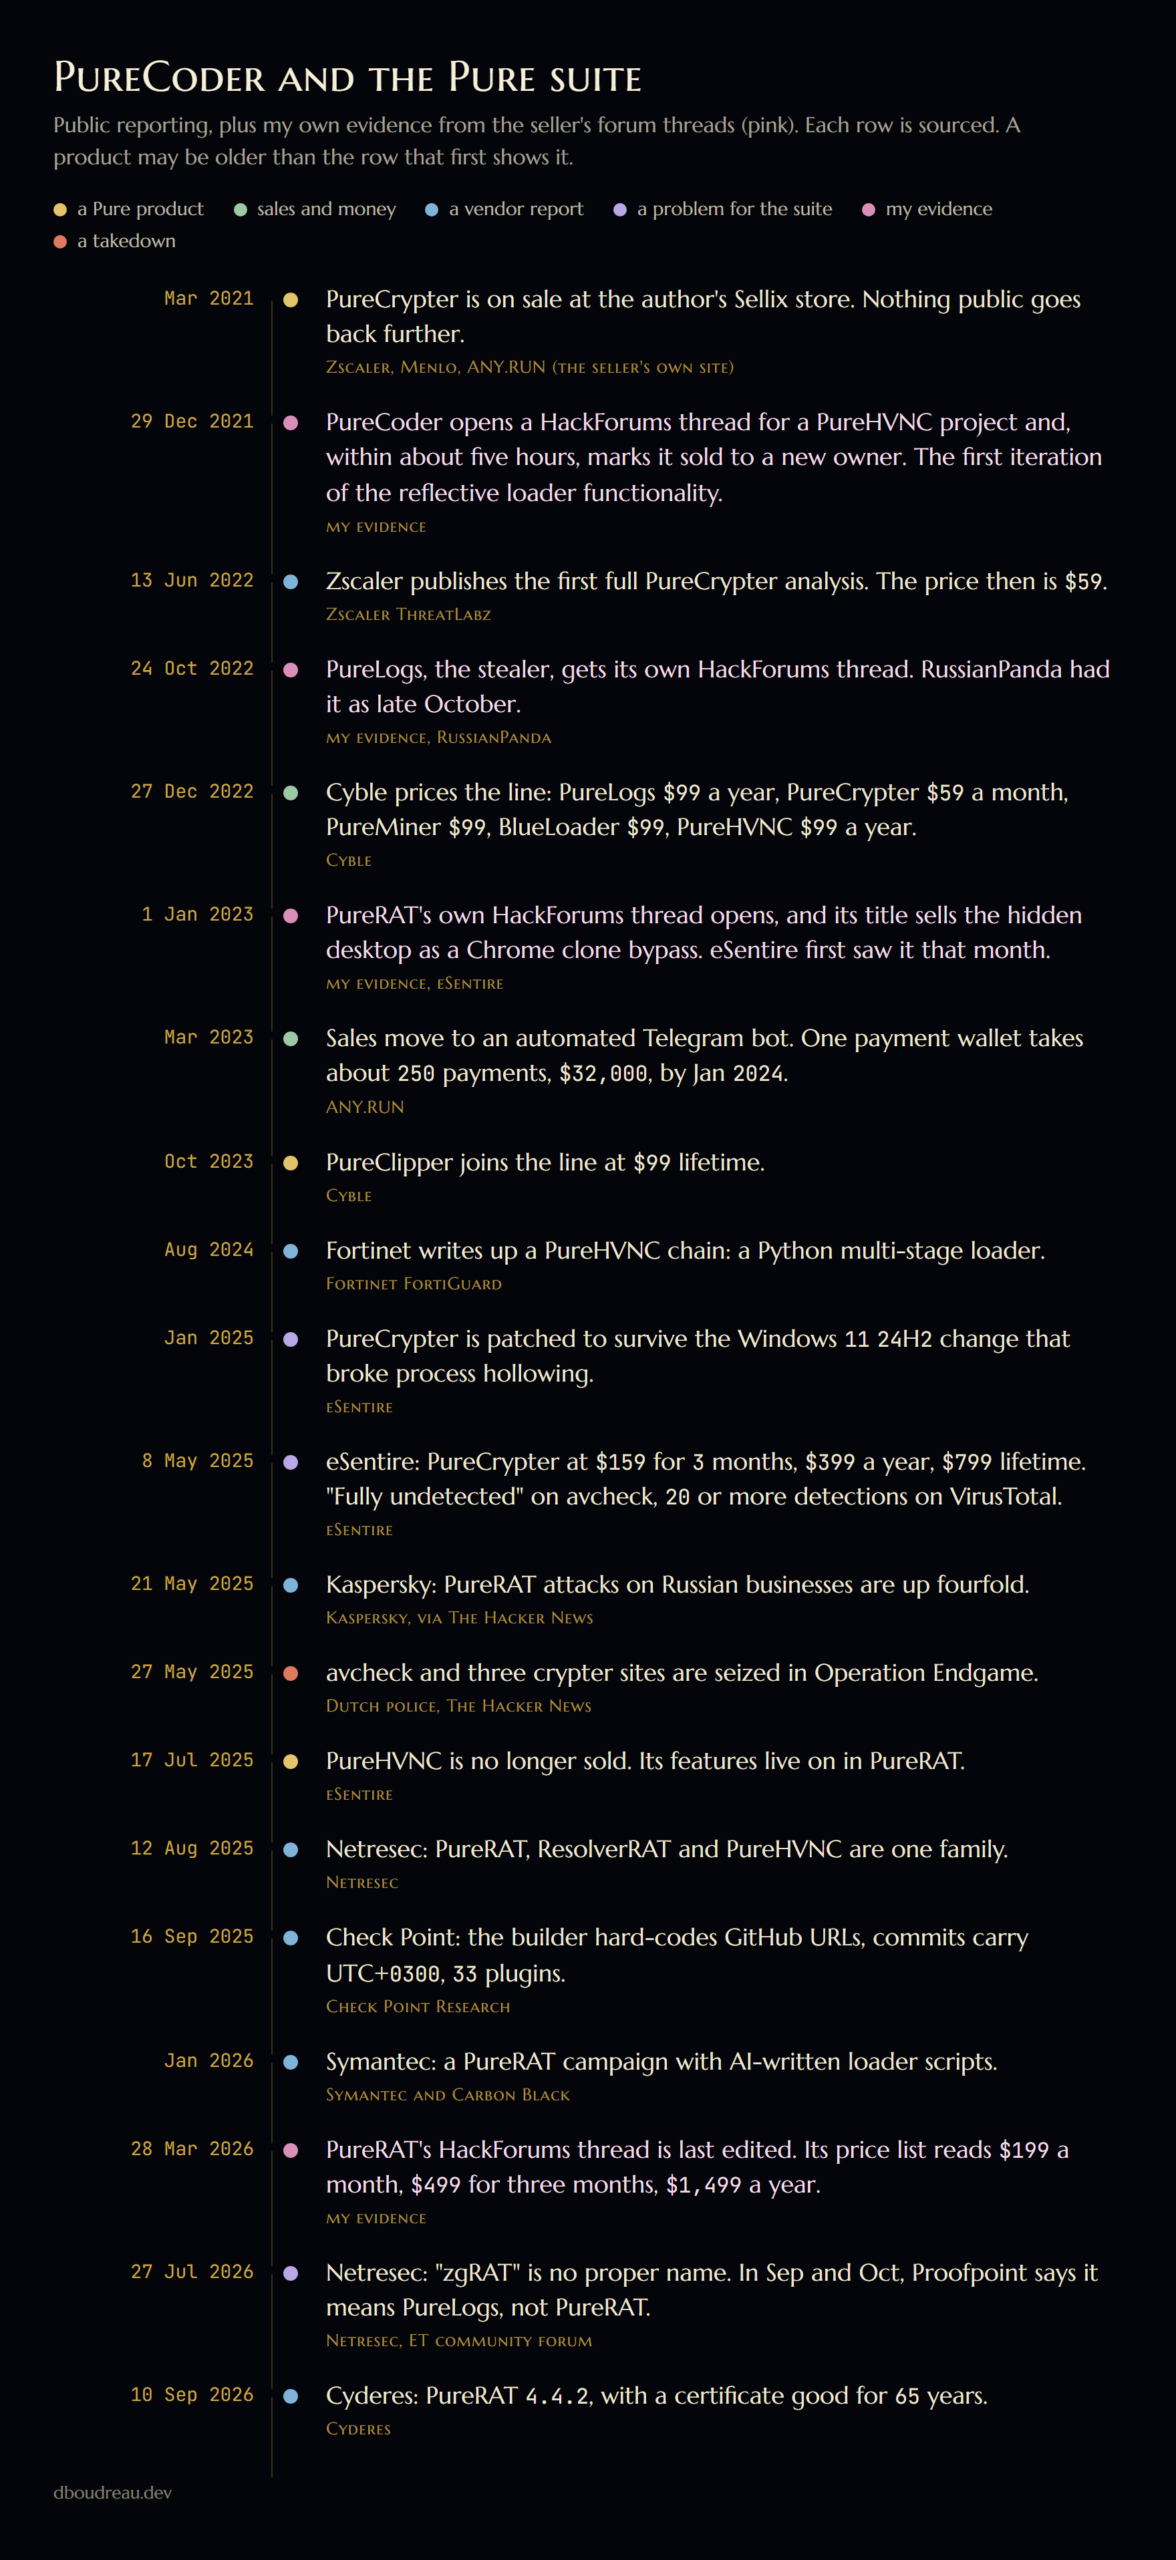
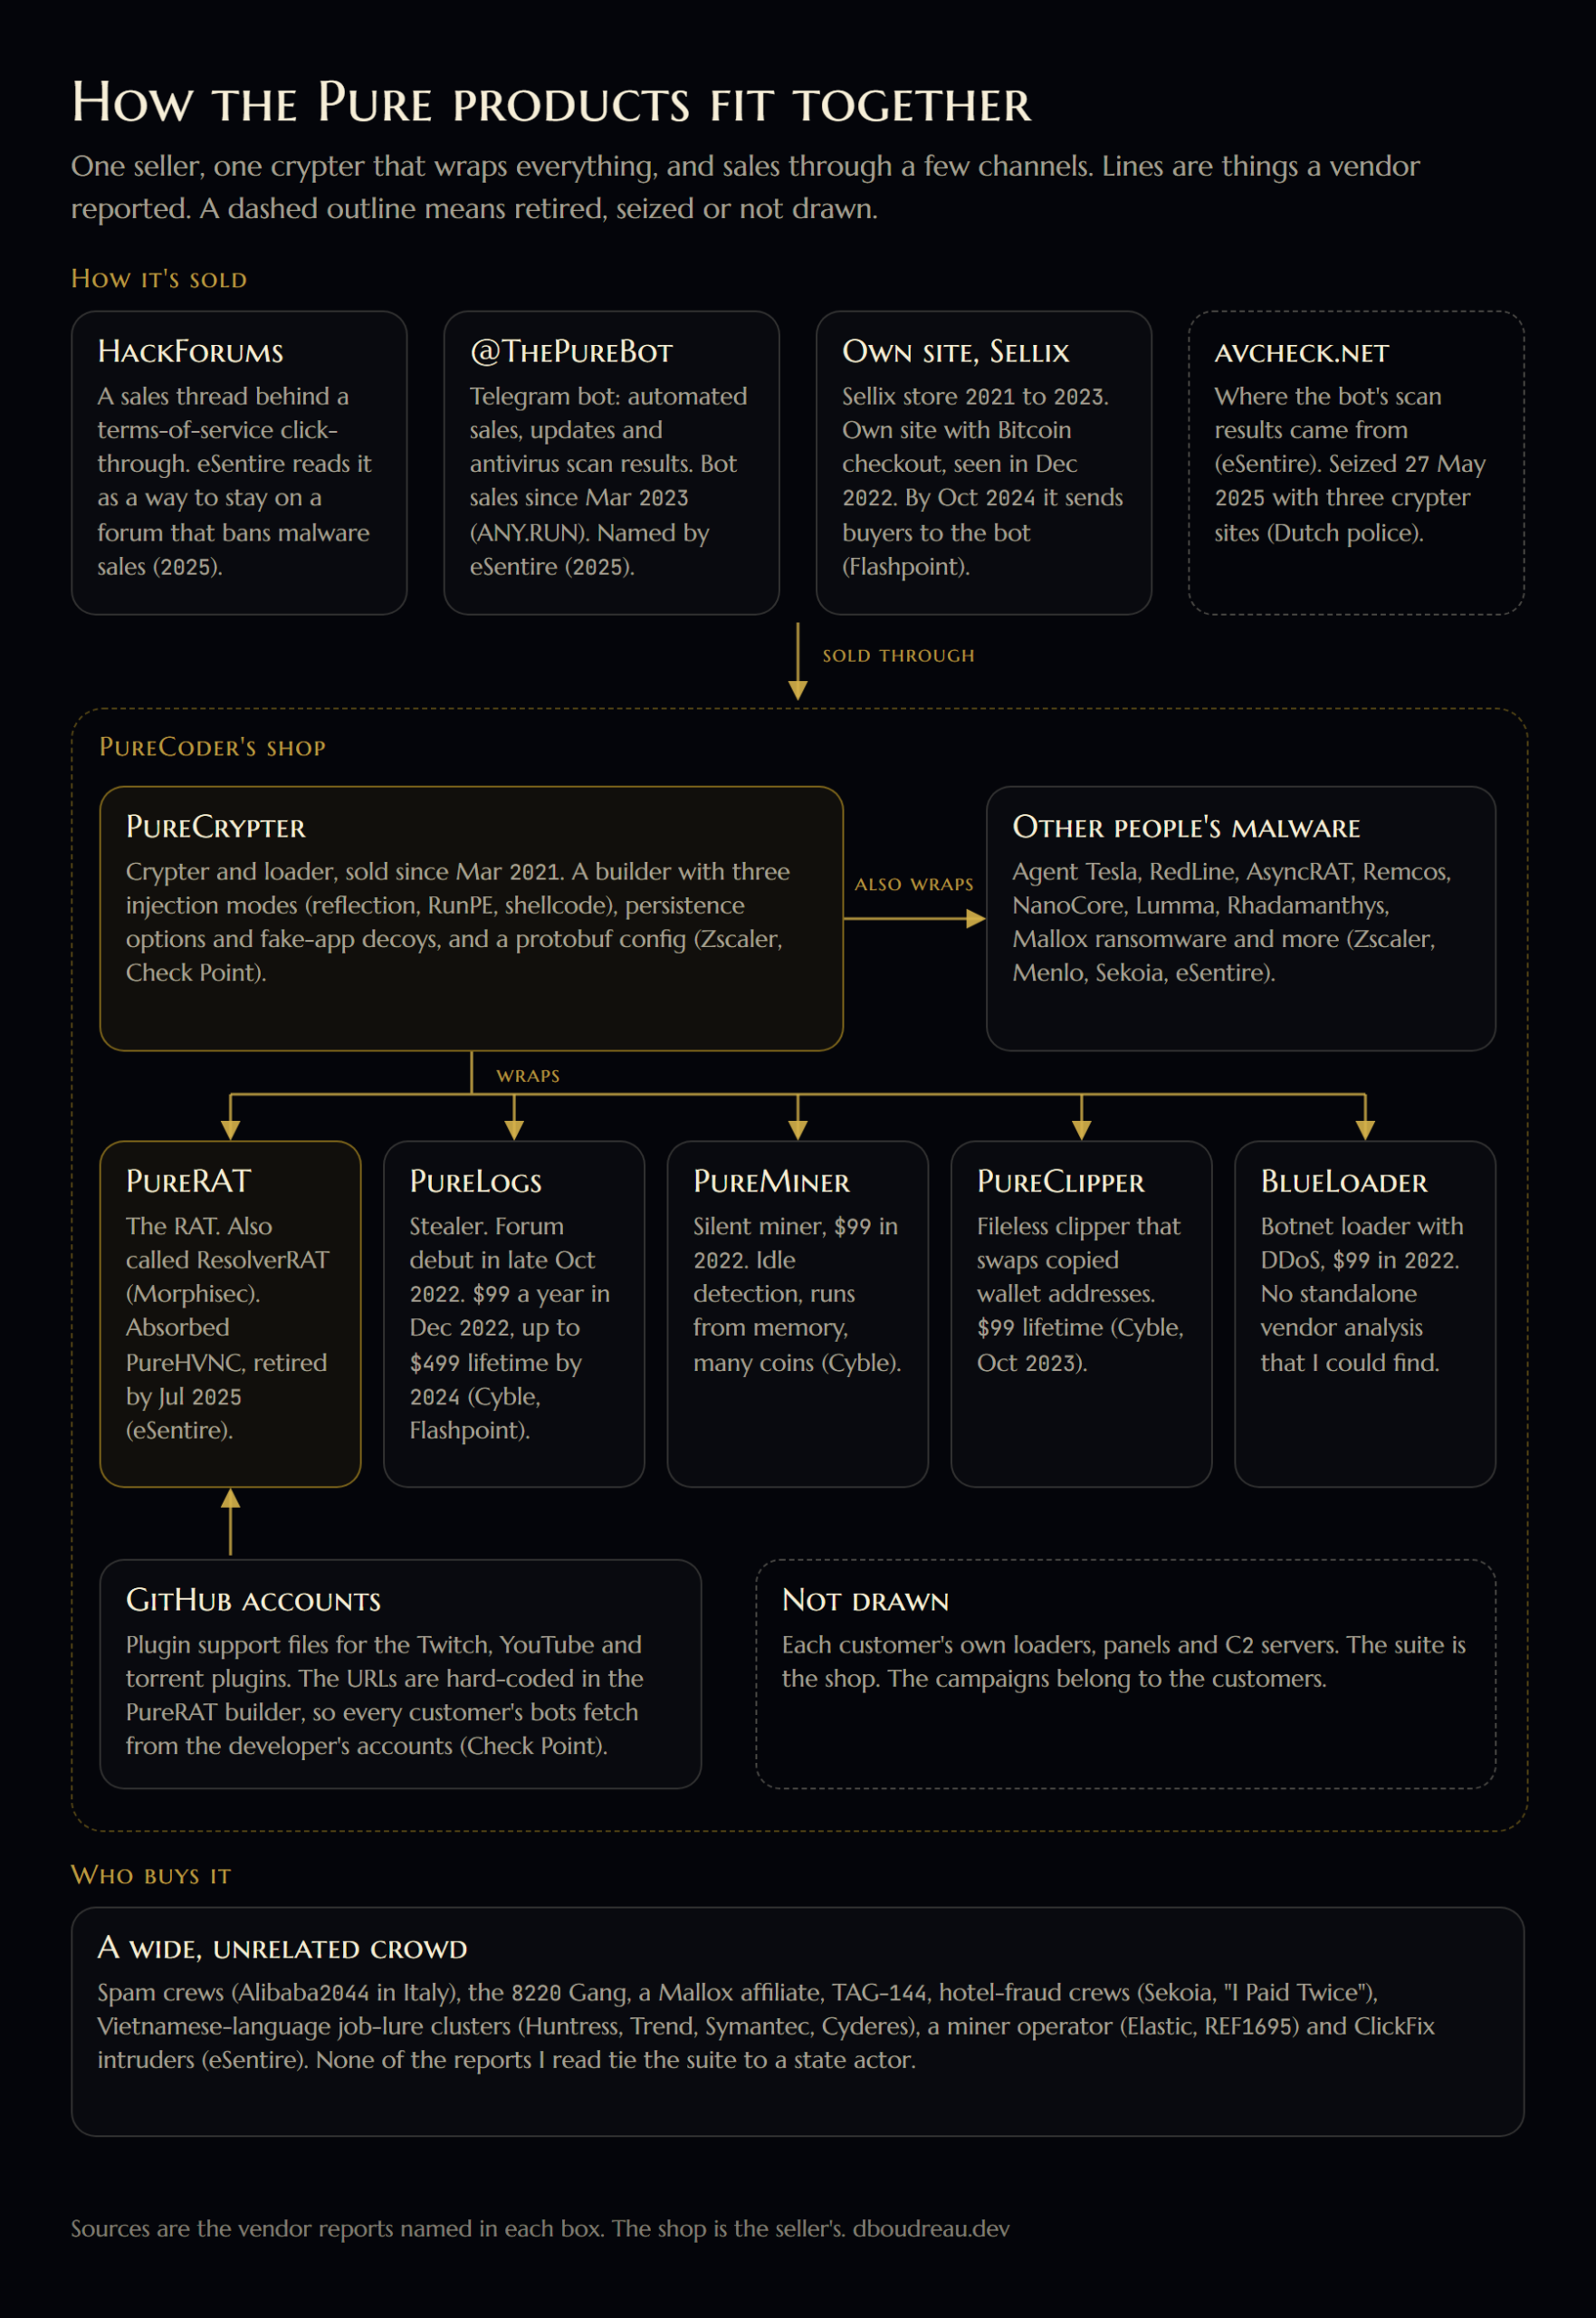
The line grew in the order vendors found it. PureLogs, the stealer, showed up on forums in late October 2022 (RussianPanda), and the seller’s own thread for it is dated 24 October (my evidence). By 27 December 2022 Cyble had a price list with PureHVNC, PureMiner and BlueLoader on it. PureRAT appeared on HackForums in January 2023 (eSentire), and the seller’s own thread for it opened on 1 January (my evidence). PureClipper followed by October 2023. Sales started on Sellix, moved to the seller’s own site with Bitcoin checkout, and from March 2023 went through an automated Telegram bot. eSentire named it @ThePureBot in 2025 and described one store for everything, with automatic updates and antivirus scan results. A HackForums sales thread sits behind a terms-of-service click-through, which eSentire reads as a way to stay on a forum that bans malware sales.
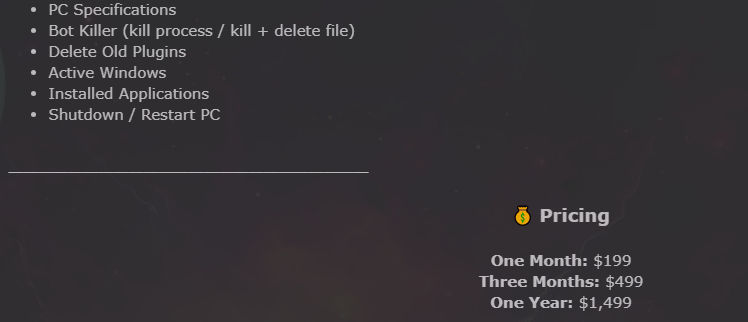
The prices moved. PureCrypter was $59 a month in 2022, then $159 for three months, $399 a year or $799 lifetime when eSentire looked in May 2025. PureLogs went from $99 a year (Cyble, December 2022) to $99 a month and up to $499 lifetime (Flashpoint, October 2024), and the seller’s own PureLogs thread now lists $150 a month, $399 for three months and $1,250 a year (my evidence). In December 2022 PureHVNC was $99 a year, and PureMiner and BlueLoader $99 each. No public report gives a PureRAT price. The seller’s own thread for it, last edited in March 2026, lists $199 a month, $499 for three months and $1,499 a year (my evidence, section 7).
The builder limits you to 30 executable packs and 3 packs of other formats every 24 hours (eSentire), and the bot sends scan results from avcheck, which is where the marketing line comes from (section 8). ANY.RUN tracked one Bitcoin wallet on the payment page: about 250 payments worth $32,000 between late May 2023 and January 2024. That’s about $128 a payment, my arithmetic, which fits the price list. One wallet in one channel is a floor, not revenue.
Context
A crypter packs or encrypts a payload so antivirus doesn’t recognise it, and a loader fetches and runs the real payload. PureCrypter does both. A stealer takes saved passwords, cookies and wallets. A clipper swaps a copied crypto address for the attacker’s. A miner mines coins on the victim’s hardware. Seller and customer are different people: the suite is the shop, and every campaign belongs to whoever bought from it.
The buyers are a wide, unrelated crowd: a spam crew in Italy (Alibaba2044), the 8220 Gang, a Mallox ransomware affiliate, TAG-144, hotel-fraud crews (Sekoia’s “I Paid Twice”), Vietnamese-language job-lure clusters (Huntress, Trend Micro, Symantec, Cyderes), a miner operator (Elastic’s REF1695) and ClickFix intruders (eSentire). None of the reports I read tie the suite to a state actor.
3. How the pieces fit
PureCrypter is the glue. It wraps the seller’s own products (Cyble lists PureMiner and PureHVNC as crypter-ready, and Check Point says it’s used to obfuscate PureLogs and PureHVNC) and everyone else’s: Agent Tesla, RedLine, AsyncRAT, Remcos and NanoCore in Zscaler’s 2022 analysis, later Rhadamanthys and Lumma, and Mallox ransomware in Sekoia’s. Elastic’s REF1695 report has a PureCrypter component in a chain that also carries PureRAT and PureMiner. Check Point found that the PureRAT builder carries the crypter’s own options, so the RAT builder ships with the crypter’s output types, injection modes, persistence choices and fake-app decoys built in.
| Product | What it is | First public anchor | Price as reported |
|---|---|---|---|
| PureCrypter | Crypter and loader, .NET, protobuf config | Mar 2021 | $59 a month (2022). $159 / 3 months, $399 / year, $799 lifetime (2025) |
| PureLogs | Stealer | Late Oct 2022 | $99 a year (2022). $99 a month to $499 lifetime (2024). $150 a month, $399 / 3 months, $1,250 / year (seller’s thread, 2026, my evidence) |
| PureHVNC | Hidden VNC RAT, retired | Dec 2021 sale thread (my evidence). Dec 2022 list | $99 a year |
| PureRAT | The RAT that took over PureHVNC | Jan 2023 | $199 a month, $499 for 3 months, $1,499 a year (seller’s thread, Mar 2026, my evidence) |
| PureMiner | Silent miner | Dec 2022 list | $99 |
| BlueLoader | Botnet loader with DDoS | Dec 2022 list | $99 |
| PureClipper | Fileless clipper | Oct 2023 | $99 lifetime |
4. PureHVNC becomes PureRAT: one lineage, three names
PureHVNC was on the price list at $99 a year in December 2022. eSentire first saw PureRAT on HackForums in January 2023, and in July 2025 reported that PureHVNC was no longer for sale, because PureCoder had folded its features into PureRAT, now the main product. Netresec states it flatly: PureRAT is the exact same malware as what Morphisec calls ResolverRAT, and PureHVNC is its predecessor. Huntress found PureHVNC namespaces inside a sample that calls itself PureRAT and describes them as legacy modules that live on in the newer products.
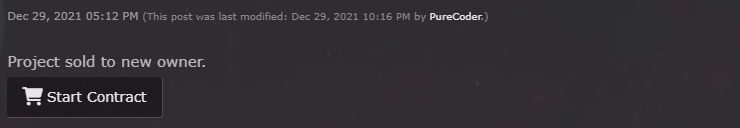
PureHVNC was sold once before it had a price list, and none of the reports I read mention it. On 29 December 2021 PureCoder opened a HackForums thread for a PureHVNC project and, within about five hours, marked it sold to a new owner (my evidence). A member replied seven minutes after the thread opened and praised the GUI, so the thread was still showing the product then. On my evidence that project was the first iteration of the reflective loader functionality. I don’t know who bought it or what changed hands. A year later PureCoder was listing PureHVNC again at $99 a year, so the later product is a rewrite, a second iteration, or the same code come back, and nothing public says which.
Vendors still split on the label. Fortinet (2024), Check Point (2025) and Malwarebytes (2026) call the payload PureHVNC. Kaspersky, eSentire, Huntress, Sekoia, Symantec, Trend Micro and Cyderes call it PureRAT. My read, which is inference and not something those reports say: PureRAT is the product and builder brand, and PureHVNC survives as the internal name of the payload. Vendors who label by library or namespace say PureHVNC. Vendors who label by builder, certificate name or marketing say PureRAT.
Two other names cause trouble. “zgRAT” is the label an old Suricata rule and a popular YARA rule put on both PureLogs and PureRAT. Netresec argued in July 2026 that it has no proper definition, and in late September Proofpoint told the Emerging Threats community it means PureLogs and not PureRAT. That YARA rule fires on any .NET Reactor binary, so don’t take a hit as family evidence. And Trend Micro first published a December 2025 job-seeker campaign as ValleyRAT, then corrected it to PureRAT nine days later.
The version strings don’t help. Elastic’s tracking has 0.3.8B (a November 2023 build label), 0.3.9 (January 2025) and 3.0.1 (January 2026). Check Point’s sample reported 4.1.9, labelled PureHVNC, and Cyderes saw 4.4.2 in 2026. That isn’t a clean sequence. Either there are two tracks, or the field is the customer’s to edit, or the numbering was reset. There’s a second puzzle in Elastic’s report: its PureRAT protects the traffic with a PBKDF2-derived key and an HMAC, and mentions no TLS, where everyone else describes pinned TLS.
The seller’s own threads add another pair of numbers. The PureRAT panel in its thread reads 4.0.9041.14924, and the PureLogs panel in another reads 5.0.9542.23248 (my evidence). If the third part is a build counter in days since 1 January 2000, which is what a default wildcard version in Visual Studio produces, those are 2 October 2024 and 15 February 2026. That’s my arithmetic, and the wildcard is my assumption, not something I’ve seen in a sample. The second date falls about six weeks before its thread’s last edit, so it fits, and that’s all it does. If it holds, the file version of a sample dates its build, and that would put the version mess in date order.
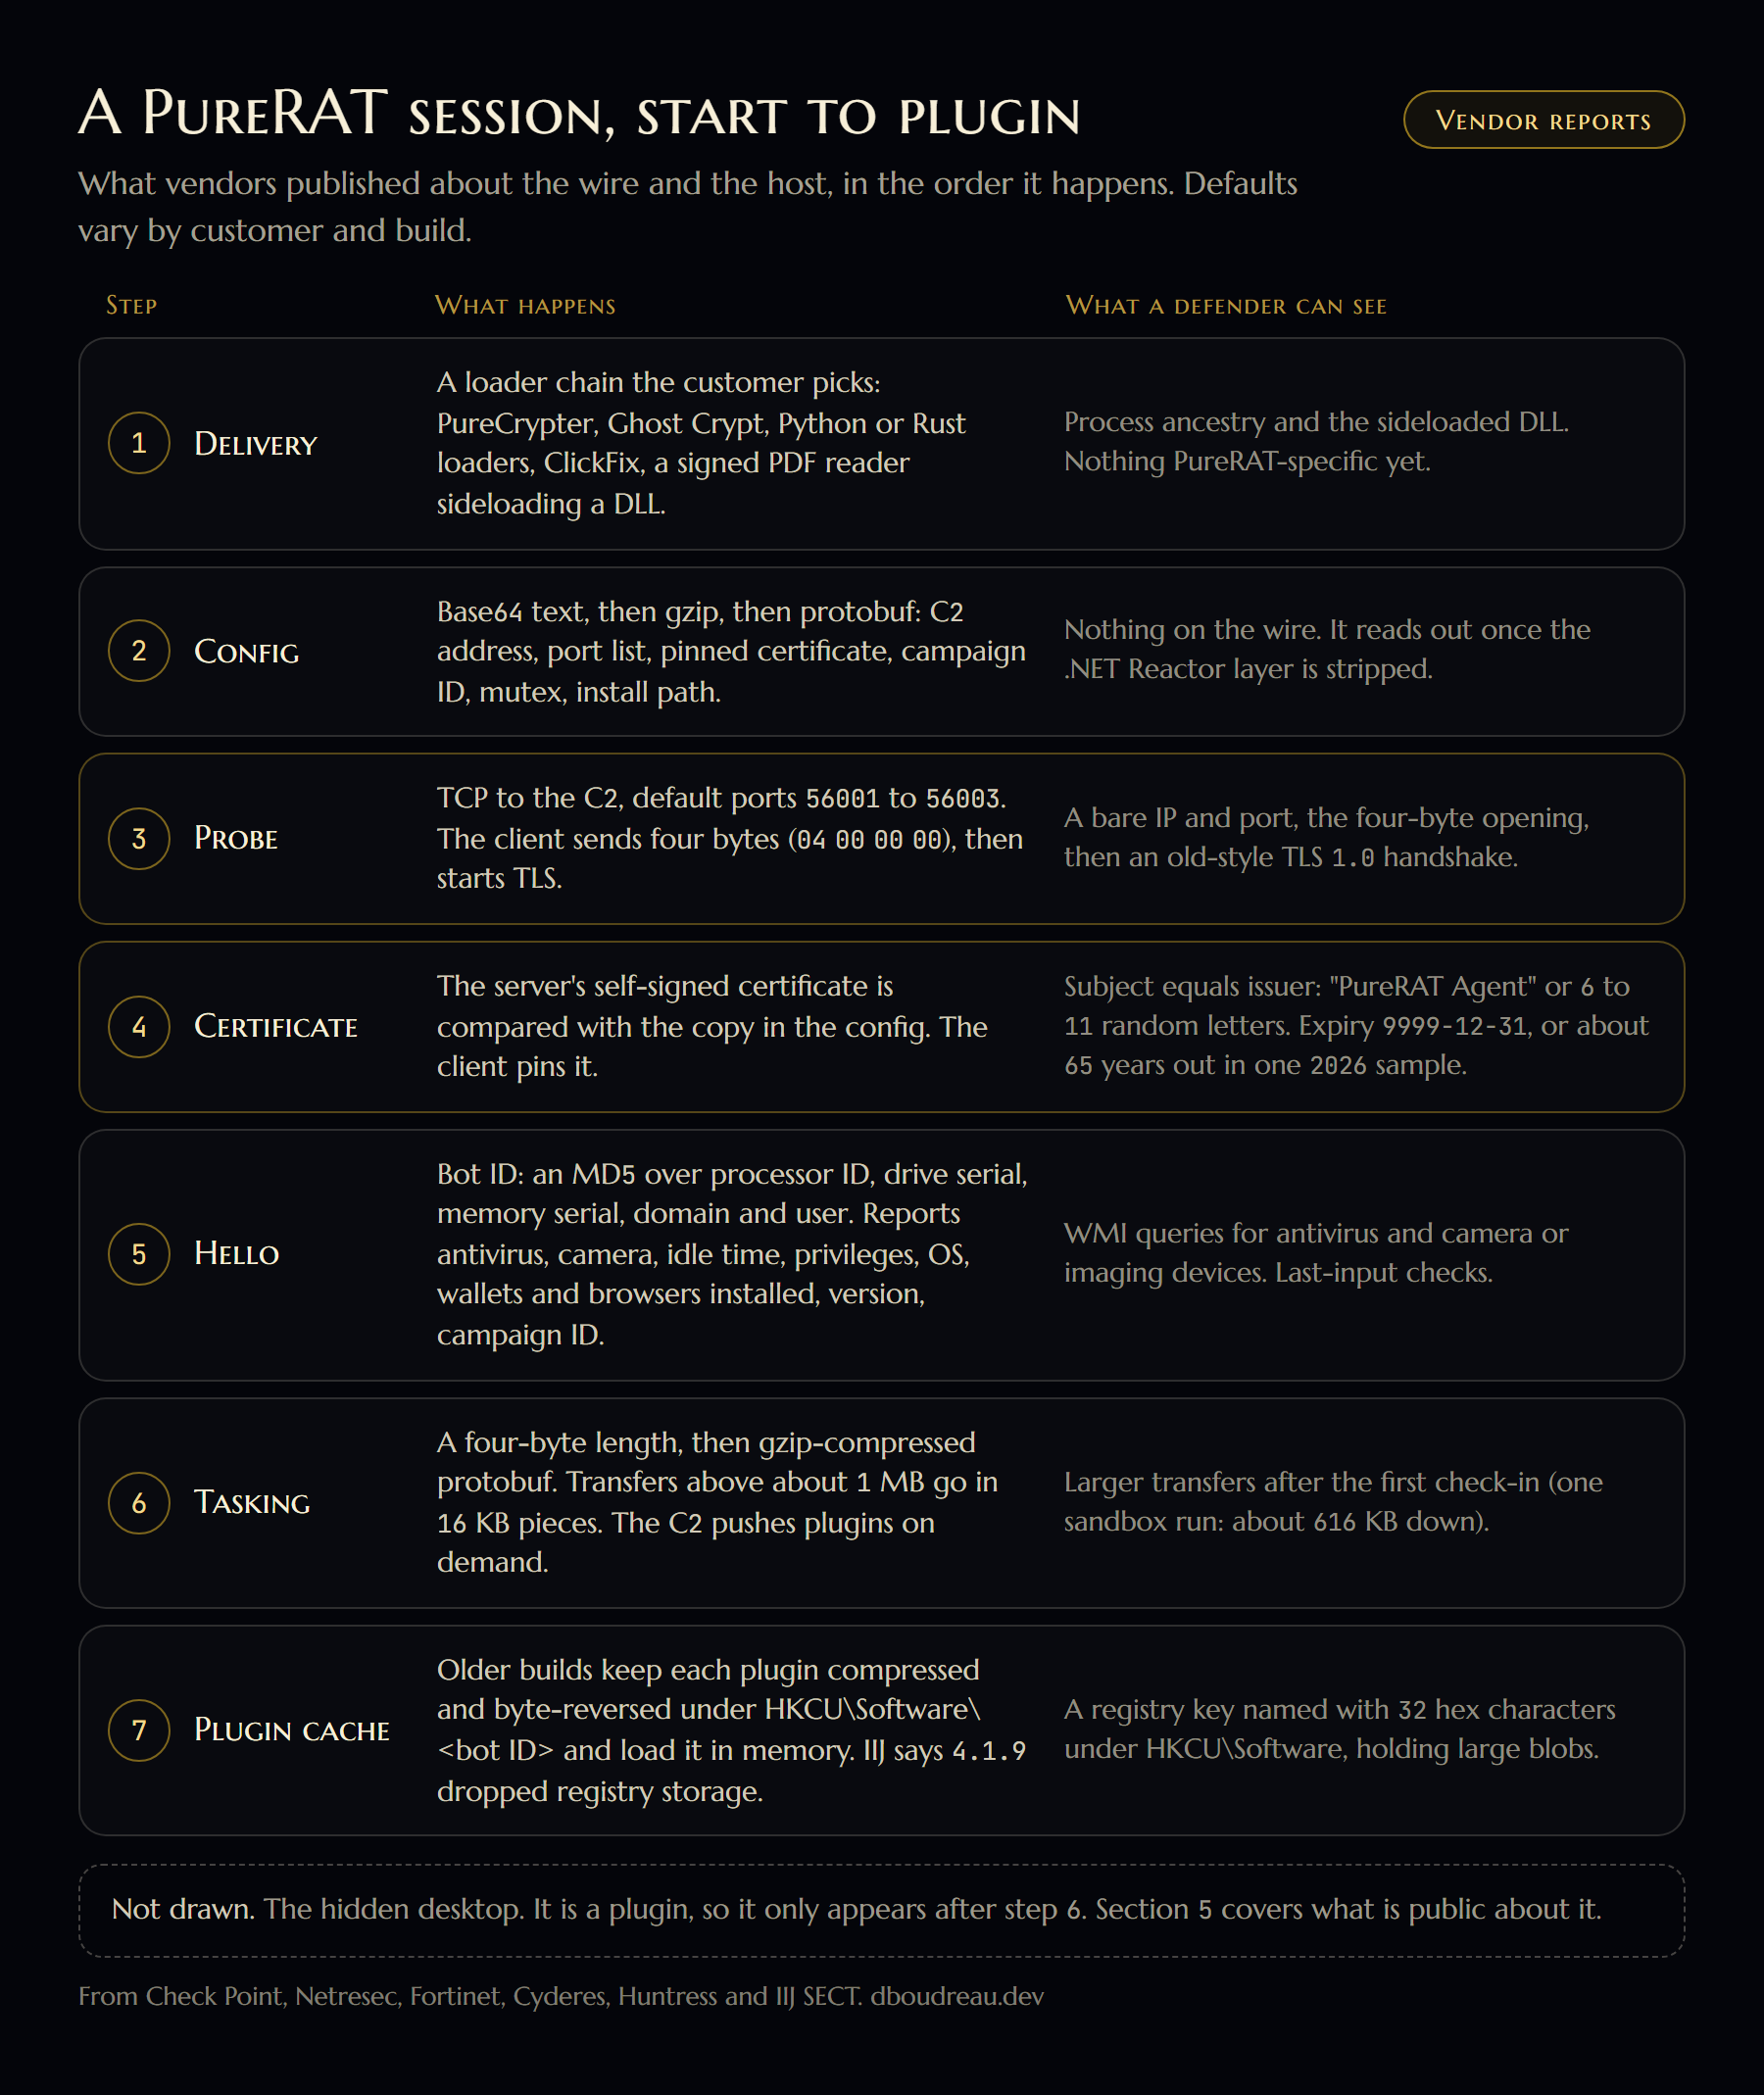
On the wire it’s a small, consistent design. The config is base64 text holding a gzip-compressed protobuf: C2 address, port list, pinned certificate, campaign ID, mutex, install path. The client connects to a C2, by default on port 56001, 56002 or 56003, sends four bytes (04 00 00 00) and starts TLS, then checks the server’s self-signed certificate against the copy in its config. Inside the tunnel it’s a four-byte length and gzip protobuf, with big transfers cut into 16 KB pieces. The bot ID is an MD5 over the processor ID, drive serial, memory serial, domain and user name, and the first message reports antivirus, camera, idle time, privileges, wallets and browsers installed, version and campaign ID. The certificate subject is either “PureRAT Agent” or a random string of six to eleven letters, and the expiry is year 9999 in most reports, though Cyderes saw about 65 years in one 2026 sample.
Context
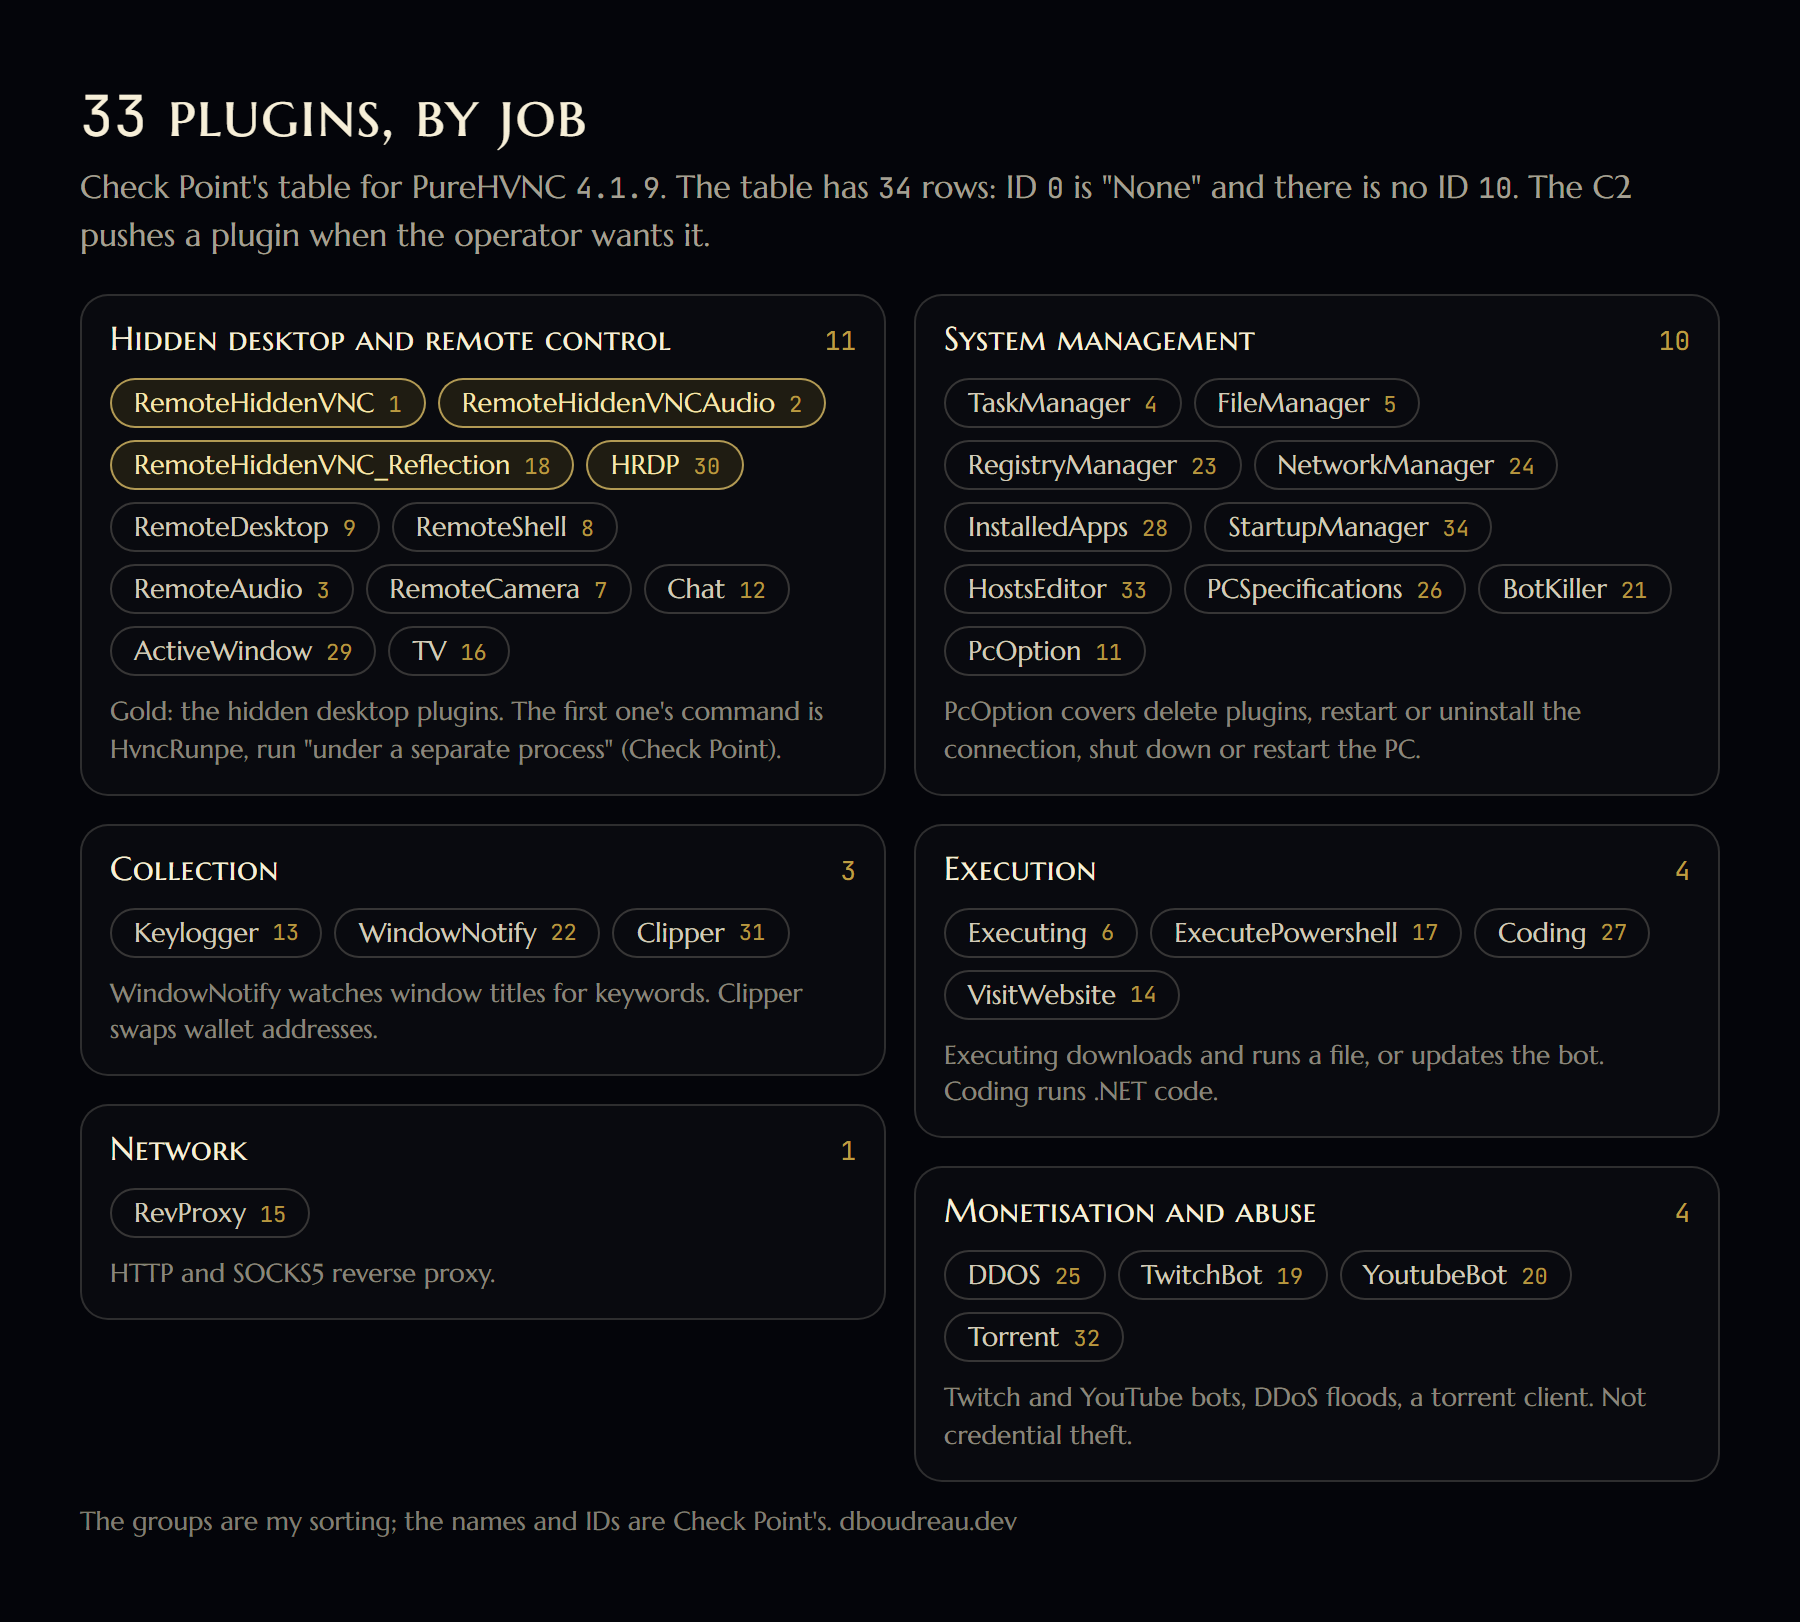
A plugin RAT keeps the stub small and pushes features after infection. Fortinet describes PureHVNC’s plugins as .NET DLLs served by the C2, loaded in memory, and in older builds cached under HKCU\Software\<bot ID>. So what a sample does on a sandbox with no live C2 is a fraction of what an operator can make it do.
The plugin list is the product. Besides the remote control and file tools, it has a clipper, a reverse proxy, a .NET code runner, a DDoS plugin, a torrent client and Twitch and YouTube bots. Those last ones fetch their browser drivers and helper files from GitHub accounts whose URLs are hard-coded in the PureRAT builder, which is the one operational slip Check Point found (section 10). My reading, which is inference: bots that follow, like and click ads mean the customer base includes view-botting and ad-fraud users, not only people stealing credentials.
5. The hidden desktop: what the public record shows
Context
Windows groups windows into desktops inside a window station. The interactive station has three by default (Default, ScreenSaver and Winlogon), and only one at a time is the input desktop, the one the user sees and types into. Window messages only travel between processes on the same desktop, and any process can create another desktop. A hidden-VNC (hVNC) tool makes one, never switches to it, starts a shell and the victim’s own browser there, streams that desktop’s pixels to the operator and replays the operator’s mouse and keyboard. Nothing is exploited. Microsoft documents every piece of it, and MITRE tracks it as T1564.003.
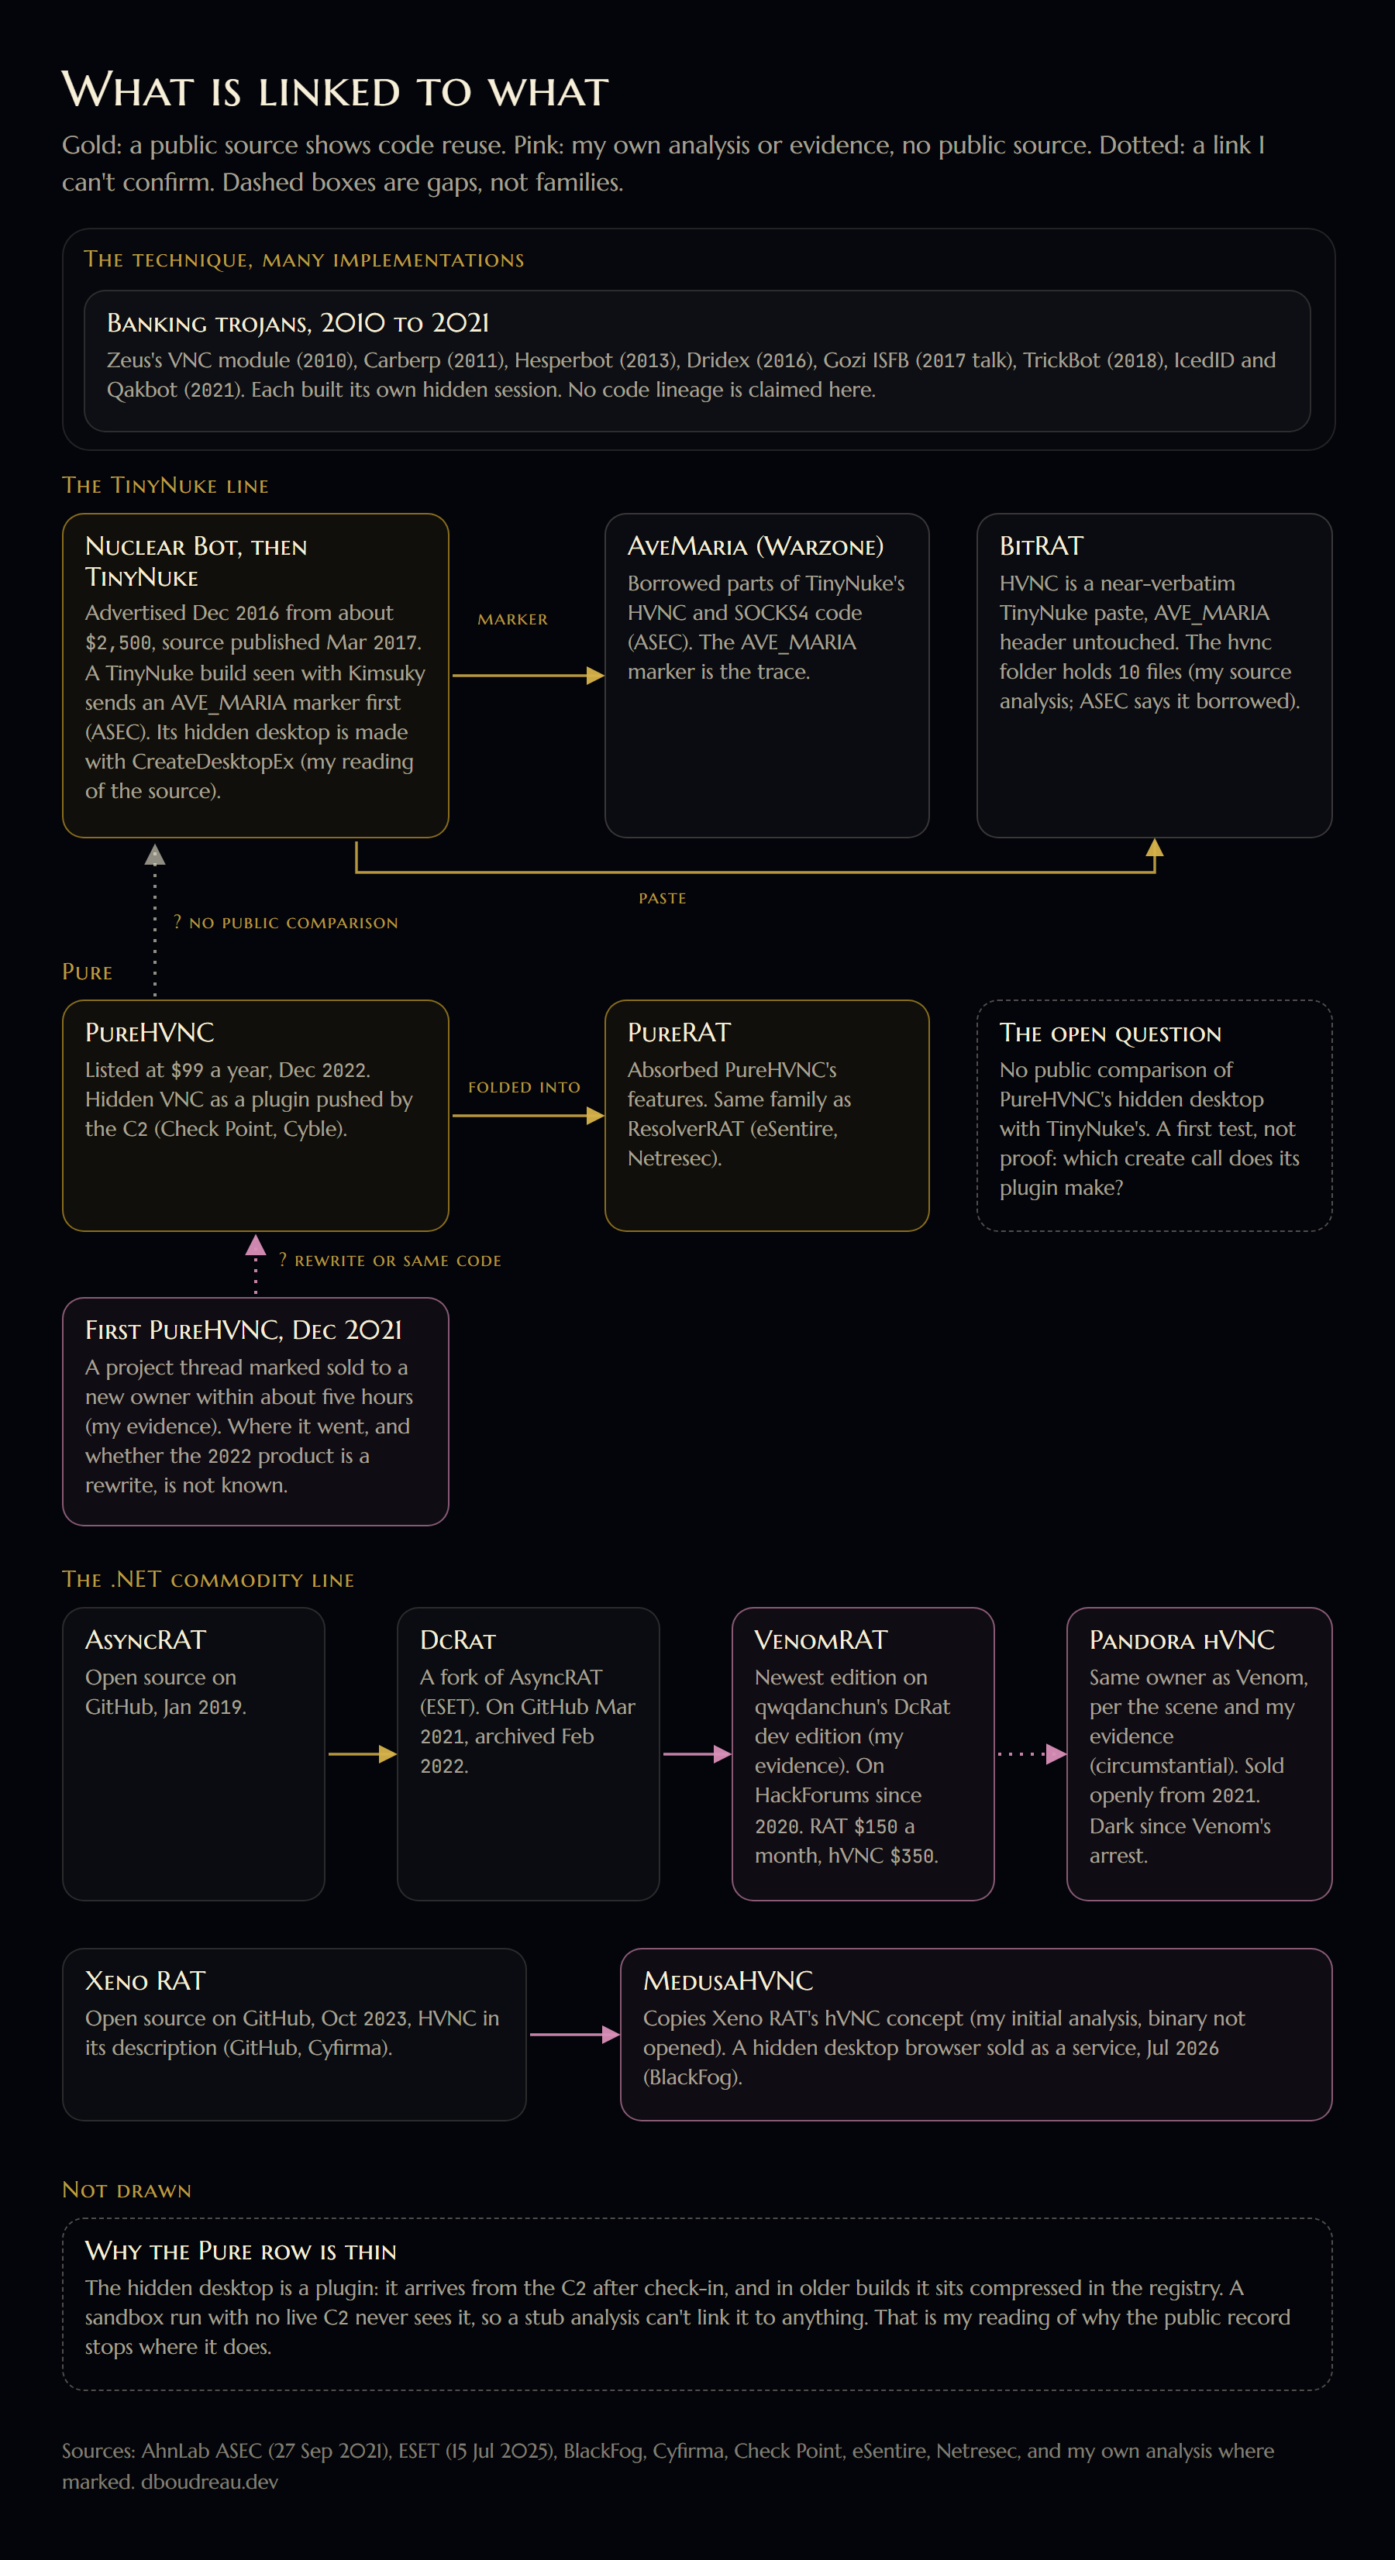
TinyNuke is the reference point for the cheap, copied kind. It’s the Nuclear Bot banking trojan: advertised from about $2,500 in December 2016, with VNC as command 1 (NETSCOUT), and its source published by the developer in March 2017. AhnLab’s ASEC found its HVNC module in a Kimsuky intrusion in 2021: reverse VNC (the victim connects out), a handshake string, AVE_MARIA, sent before the session starts, and a second explorer.exe running as a child of the first. ASEC says recent samples use a different string, “LIGHT’s BOMB”, and that AveMaria and BitRAT borrowed parts of its HVNC and SOCKS4 code. I can back the BitRAT half from my own work: in my analysis of the leaked BitRAT client source, its HVNC is a near-verbatim TinyNuke paste with the AVE_MARIA header left untouched, and its hvnc folder holds ten files.
On my reading of TinyNuke’s source, its hidden desktop is made with CreateDesktopEx. Hold that thought, because it’s the one detail that makes a lineage test cheap. No vendor report names that call for any family.
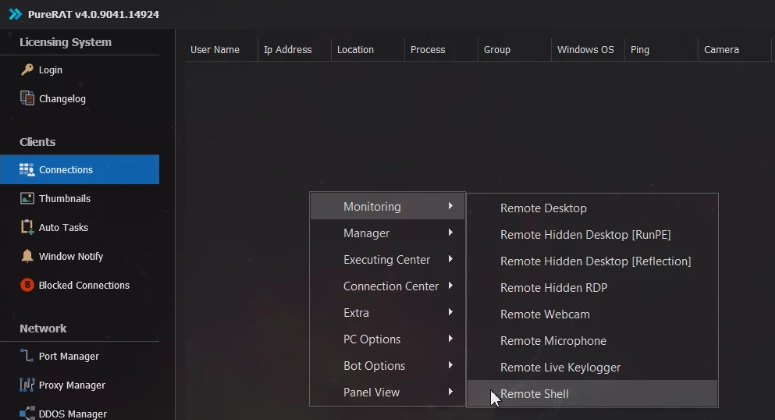
For PureHVNC, the public record is one table and a few adverts. Check Point’s plugin table lists RemoteHiddenVNC (ID 1, command HvncRunpe, running “under a separate process”), RemoteHiddenVNCAudio (ID 2), RemoteHiddenVNC_Reflection (ID 18), HRDP, a hidden RDP (ID 30), and a plain RemoteDesktop (ID 9). Check Point doesn’t say how the hidden desktop is made, what it’s called or what runs on it. The seller’s own v4 panel (my evidence) lists the hidden desktop twice, as Remote Hidden Desktop [RunPE] and Remote Hidden Desktop [Reflection], beside a hidden RDP entry and a plain Remote Desktop. The seller’s own advert, as Cyble read it in December 2022, claims hidden VNC for Chrome, Edge, Brave, Firefox, Outlook and Foxmail, CMD and PowerShell, clipboard, DPI and a run-program box, a task and file manager, “runs on RAM, no dropping files” and a .NET 4.0 stub. That’s marketing. Huntress lists hidden desktop access among PureRAT’s advertised features and notes it never saw it used, because its SOC isolated the host before the operator pushed a single plugin. Symantec found a Python loader that injects “HVNC shellcode” into a suspended InstallUtil.exe, and says nothing about where that shellcode came from. Fortinet’s analysis describes the plugin architecture and a PluginRemoteDesktop with mouse control, and no hidden desktop.
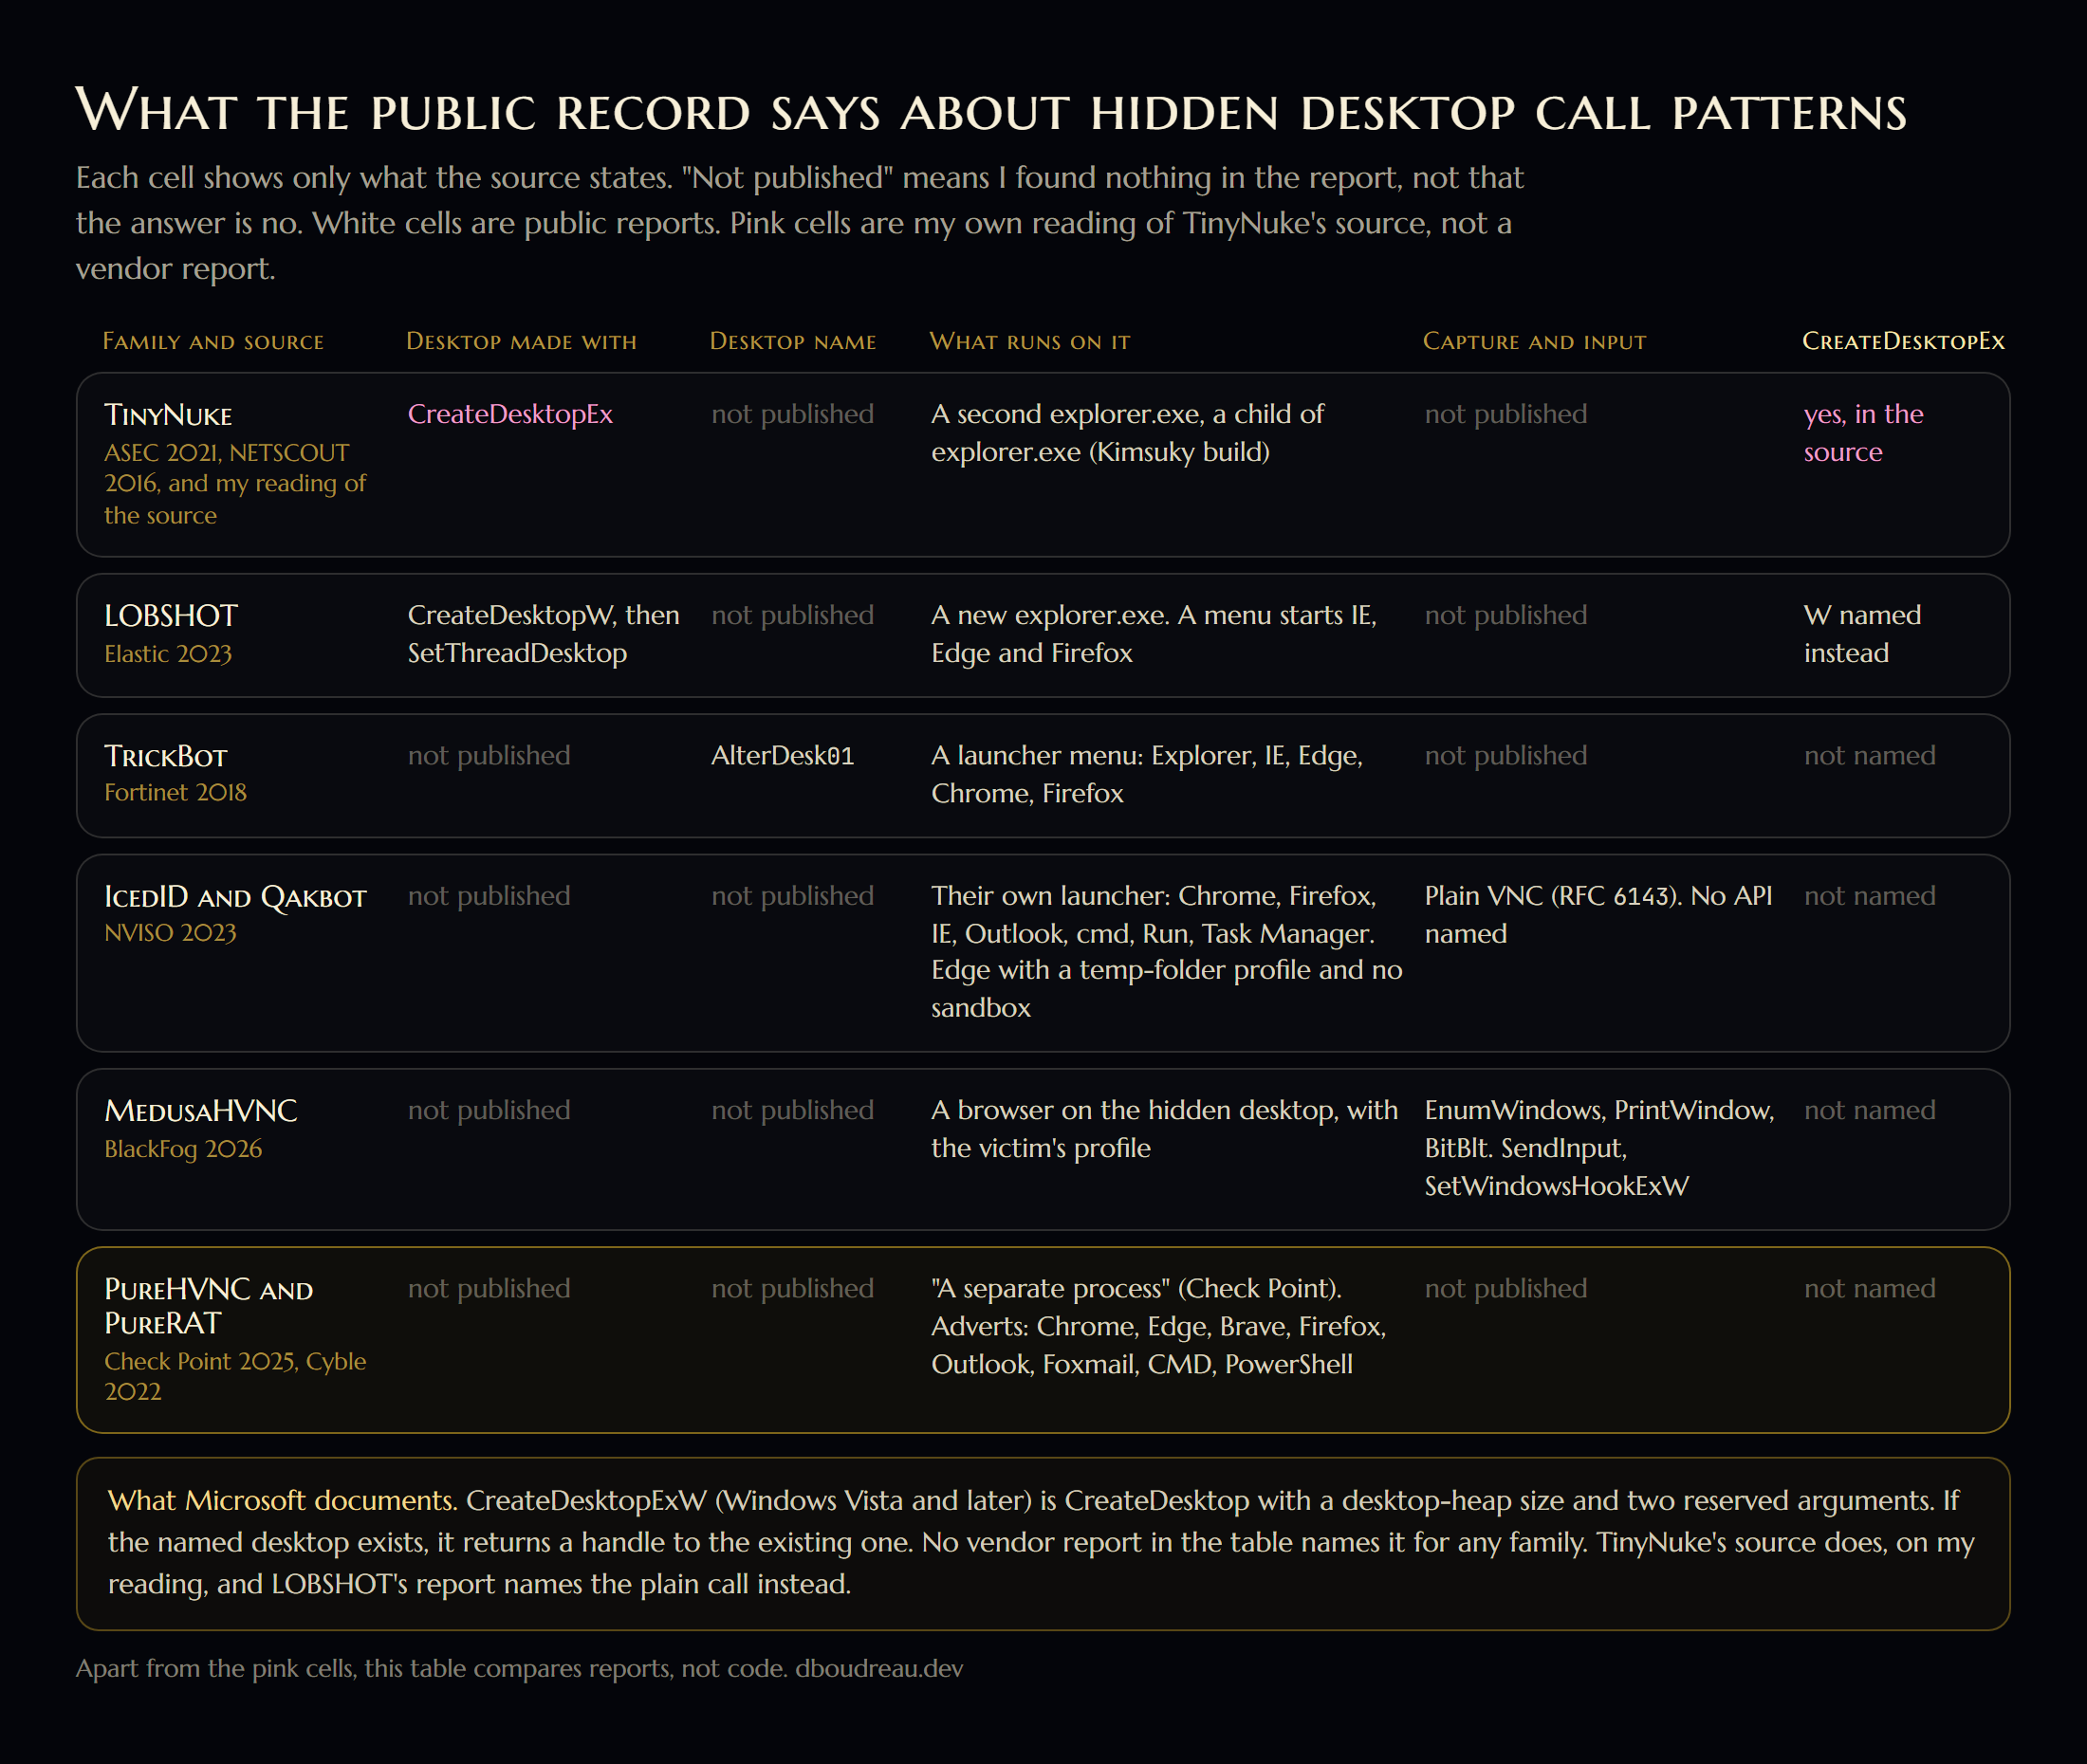
Here is why the record is thin, and it’s my reading. The hidden desktop is a plugin. It arrives from the C2 after check-in, and in older builds it sits compressed in the registry. A sandbox run with no live C2 never sees it, so an analysis of the stub can’t say anything about how it makes a desktop. Public analyses of other families name APIs because their hidden-desktop code ships in the sample. Elastic’s LOBSHOT report names CreateDesktopW and SetThreadDesktop, a new explorer.exe on the hidden desktop and a menu that starts Internet Explorer, Edge and Firefox. BlackFog’s MedusaHVNC report names only the capture and input calls (EnumWindows, PrintWindow, BitBlt, SendInput, SetWindowsHookExW). Fortinet’s TrickBot report gives the desktop name, AlterDesk01, and NVISO’s IcedID and Qakbot report describes launcher menus and a browser started with a temp-folder profile and its sandbox off, with no API named at all.
Context
CreateDesktopExW (Windows Vista and later) is CreateDesktop with a desktop-heap size and two reserved arguments added. If a desktop of that name already exists, it returns a handle to the existing one. The number of desktops is limited by the desktop heap. Microsoft documents both calls, in ANSI and Unicode forms, and I haven’t verified how the entry points relate inside Windows, so test on your own builds before assuming a hook on one covers the others.
So the answer to “does PureHVNC use CreateDesktopEx” is that nobody has published it, and the stub can’t tell you. The question is worth asking anyway. If TinyNuke makes its desktop with CreateDesktopEx and BitRAT is a near-verbatim paste of it, that call is a marker of the TinyNuke line, and LOBSHOT’s plain CreateDesktopW is not. A PureHVNC plugin that makes its desktop with CreateDesktopEx would point toward TinyNuke’s code. One that uses the plain call would point away. It’s a first test and not proof: a rewrite can keep the call, and an unrelated tool can use it.
The command name HvncRunpe and the panel’s [RunPE] label say the hVNC server is started as a PE in a separate process, by process hollowing. The [Reflection] label points to the other way, loading from memory inside a .NET process, which is my reading of the word. RunPE and Reflection are also two of the three injection methods PureCrypter’s builder offers, and Check Point found those options inside the PureRAT builder, so my reading is that the hidden desktop plugin borrows the crypter’s loaders. That’s how the hVNC is started and not how its desktop is made, so the create-call question stays open. It fits Fortinet’s finding that the Executing plugin can inject a binary into a target process by hollowing. A RunPE launch would also suit a native hVNC server in the TinyNuke line, since BitRAT drops its own hvnc.exe, and that is the part nobody has looked at in public. On my evidence the first iteration of the reflective loader functionality was the PureHVNC project sold in December 2021 (section 4).
What I couldn’t check
This post compares reports, not code, apart from my reading of TinyNuke and my earlier BitRAT work. I haven’t seen a PureHVNC hidden-desktop plugin, and no public report shows one. Check Point’s table gives the Reflection variant (ID 18) a description that doesn’t match its name. The seller’s own menu does list a Reflection mode, so the name looks right and the description may be the misaligned part. Defender’s DeviceProcessEvents table, as Microsoft documents it, records the session and remote-session of a process and nothing about which desktop it runs on.
6. Is it AsyncRAT?
The comparison comes up in almost every thread about PureRAT. AsyncRAT is an open-source C# RAT published on GitHub by the handle NYAN-x-CAT in January 2019, under the MIT licence. It’s serialised with MessagePack, keeps its settings AES-encrypted, talks over TLS with an embedded self-signed certificate (the default subject is “AsyncRAT Server”), and has the server push plugins by hash, which the client caches in the registry under a per-victim ID and runs in memory (SonicWall described the mechanism in 2022). The forks are many: DcRat, VenomRAT and dozens more, which ESET calls a labyrinth.
Does Pure share code with it? No public analysis says so. Check Point, Fortinet, eSentire, Huntress, both Netresec posts and Morphisec make no comparison. The one sentence that does, in a derp.ca analysis of PureLogs, says PureCoder’s toolkit includes repackaged commodity RATs, and cites nothing. What does exist is shared customers and shared tooling. Fortinet saw one phishing chain deliver XWorm, VenomRAT, AsyncRAT and PureHVNC with the same packing, and Zscaler found PureCrypter carrying AsyncRAT as a payload as early as 2022. Customers, not code. The seller’s own thread for the RAT says it’s built from scratch and offers a plugin SDK for customers’ own features (my evidence). That’s marketing, and it’s the only statement from the seller about the code’s roots that I’ve seen.
| AsyncRAT | Quasar | PureHVNC and PureRAT | My reading | |
|---|---|---|---|---|
| Serialisation | MessagePack | Protocol Buffers (README) | Protobuf, gzipped on the wire | Different |
| Transport | TLS, embedded self-signed cert | TLS (README) | TLS, cert pinned to the config | Same design idea |
| Plugins | Pushed by hash, cached in the registry | Not checked | Pushed by the C2, older builds cache in the registry, bytes reversed | Same family, different details |
| Machine ID | A hardware-ID string | Not checked | MD5 over WMI values, domain and user | Different recipe |
| Plugin names | 13 folders | Not checked | 33 plugins. Chat, FileManager, RemoteCamera and RemoteDesktop match exactly | Generic names, weak evidence |
| Hidden desktop | None. RemoteDesktop is visible | None in MITRE’s entry | RemoteHiddenVNC, its audio variant, HRDP | Pure’s selling point |
My read, which is inference resting on those public facts: PureHVNC and PureRAT look like independently written .NET RATs in the same design family as AsyncRAT, a family that AsyncRAT’s 2019 release helped define. The wire design (protobuf over TLS) matches current Quasar’s stated choices more than AsyncRAT’s. One more hint cuts the other way: the Emerging Threats team noticed that both PureRAT and AsyncRAT often use certificates that match the same AsyncRAT-style rule. Strength: moderate for “same design family”, weak to none for “shared code”. What would settle it is a binary-level comparison of class names, crypto helpers and plugin entry points, the kind of evidence ESET used to show AsyncRAT shares its crypto classes with Quasar. That needs samples, and this post has none.
7. Why hidden desktops got cheap
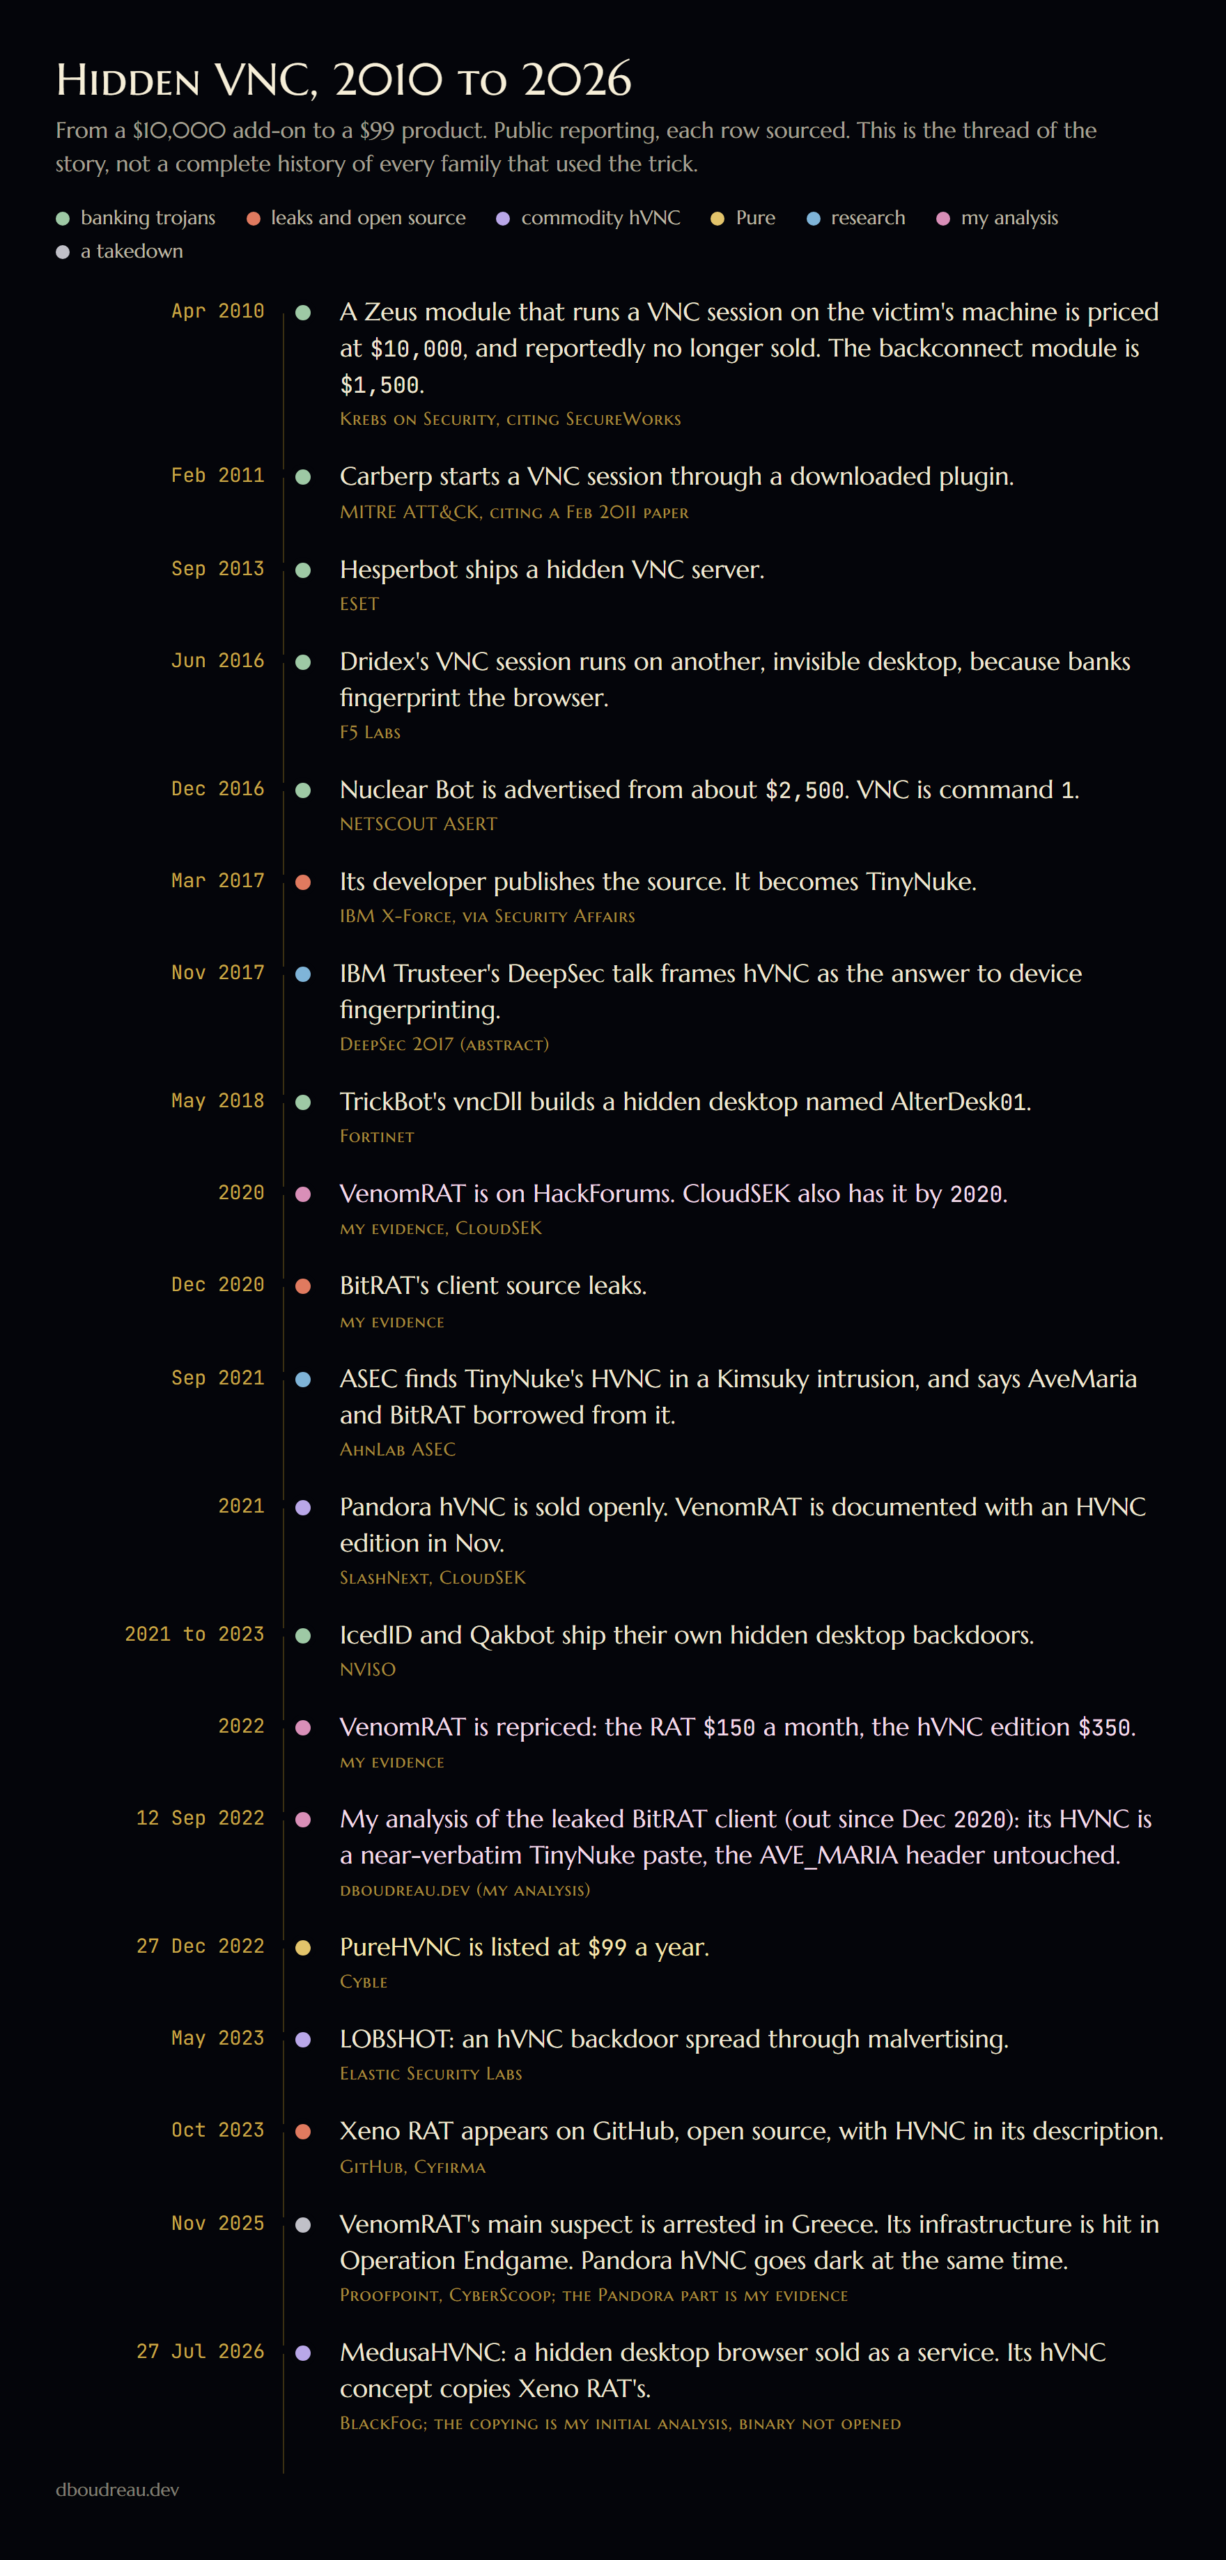
The trick is old and the price keeps changing. Krebs, citing SecureWorks, priced a Zeus VNC module at $10,000 in 2010, and reported it as no longer sold. Nuclear Bot with VNC included was about $2,500 in 2016. A few months later the developer published the source, after being labelled a scammer on the forums (IBM X-Force, via Security Affairs), and the price became zero for anyone who could compile it. Xeno RAT, an open-source RAT with HVNC in its description, appeared on GitHub in October 2023.
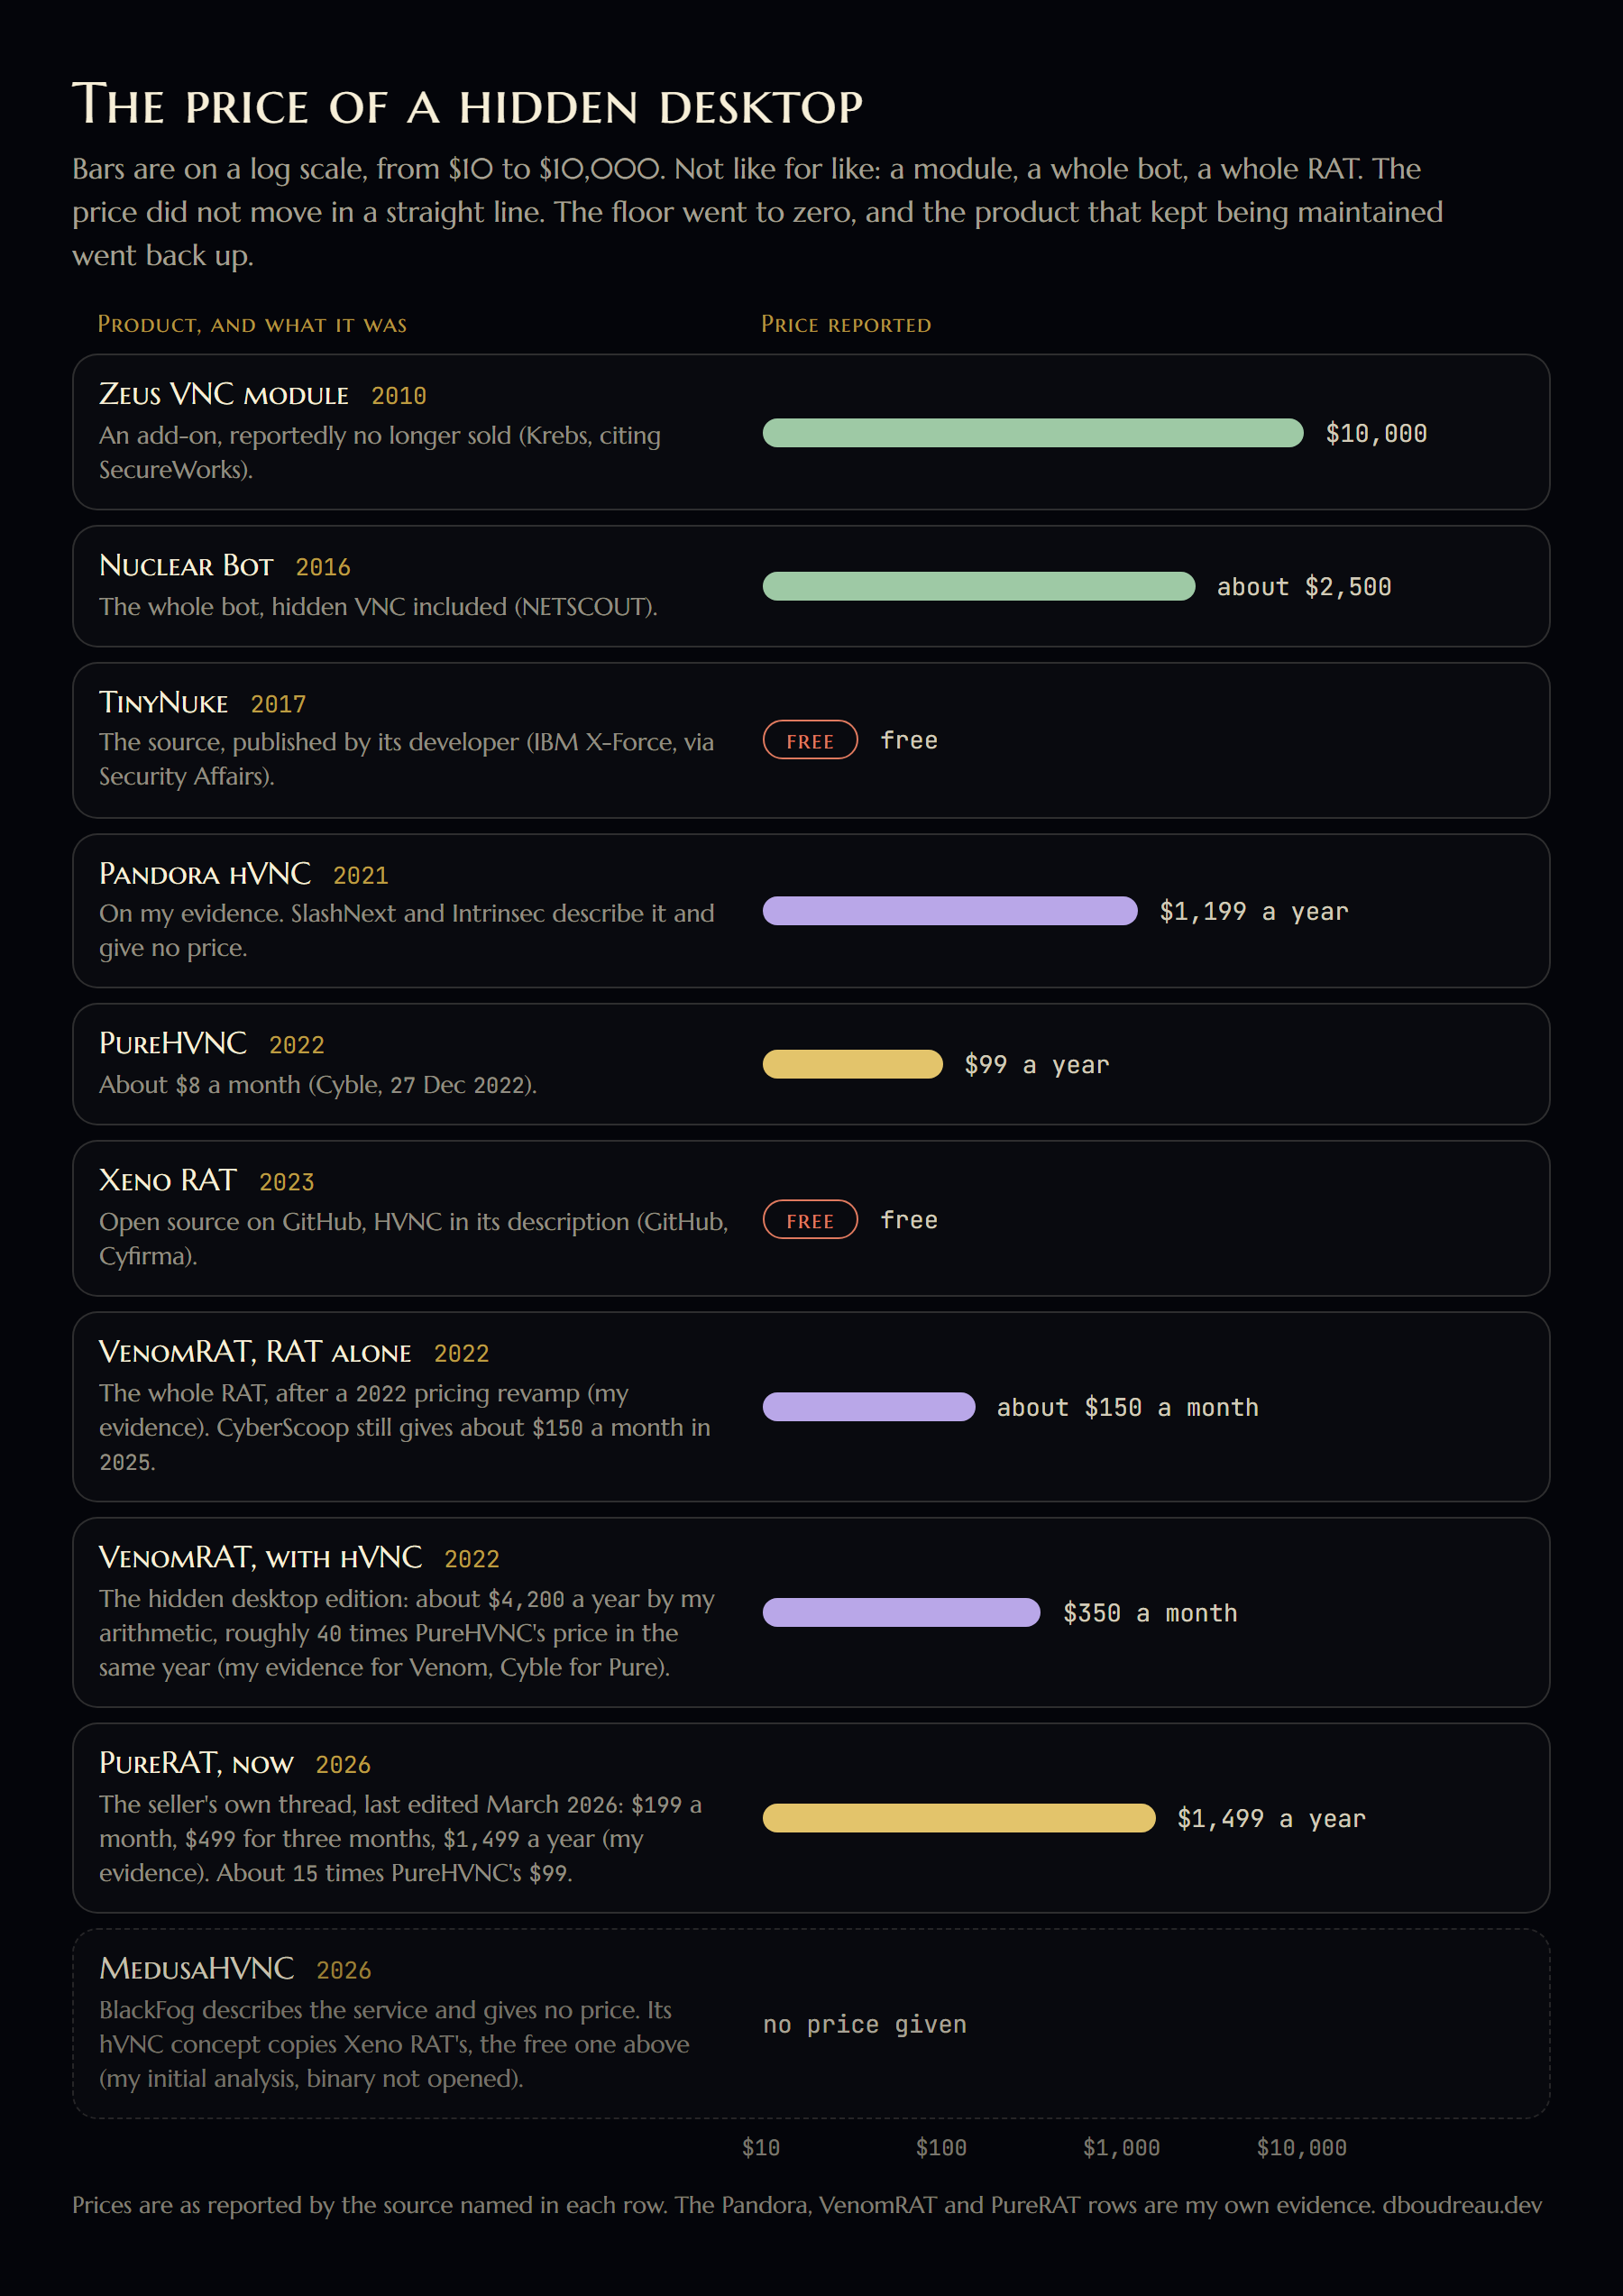
It isn’t a smooth fall, though. In 2022 PureCoder listed PureHVNC at $99 a year. On my evidence, VenomRAT was repriced the same year at $150 a month for the RAT alone and $350 a month for the hidden desktop edition. That’s about $4,200 a year, my arithmetic, roughly 40 times PureHVNC. Pandora hVNC, on my evidence, was $1,199 a year, about 12 times PureHVNC’s price, so Pure came in as the cheap option. And PureRAT is now priced at $199 a month, $499 for three months and $1,499 a year on the seller’s own thread, last edited in March 2026 (my evidence). A year is about 15 times PureHVNC’s $99 and $300 more than Pandora hVNC asked. My read is that’s what you’d expect from the one product in this story that kept getting updated: 33 plugins, a builder in three languages, a bot, a crypter built in. No public report gives a PureRAT price.
VenomRAT is the other half of the commodity market. It has been on HackForums since 2020, on my evidence, and CloudSEK had it by 2020 as well. CloudSEK documented two editions in November 2021, a plain one and one with HVNC, and in November 2025 its main suspect was arrested in Greece, with its infrastructure hit in Operation Endgame. ESET calls it likely inspired by DcRat, Proofpoint and CloudSEK describe it as Quasar-based, and on my evidence its newest edition is built on qwqdanchun’s DcRat, the dev edition.
One more link, and it’s mine, not a public report’s. In the scene, Pandora hVNC is treated as VenomRAT’s owner selling into the same market a second time. The timing fits: on my evidence Pandora went dark when Venom’s main suspect was arrested in November 2025, and on my analysis both families reskin their GUIs with the same two commercial .NET toolkits, Bunifu and Guna2. That is circumstantial. Two popular UI libraries and a shared disappearance aren’t a hard link, so this is a lead and not a finding until there is shared code, infrastructure or payment data to point at. SlashNext and Intrinsec describe Pandora as sold openly since 2021, with a browser profile cloner and a feature list built around the victim’s browser, and I wrote up the family in 2021 in PandorahVNC.
MedusaHVNC, the 2026 service BlackFog described, copies Xeno RAT’s hVNC concept, on my initial analysis without cracking open the binary. That’s a service sold on top of a free codebase (common in the MaaS market), which is the whole commoditisation story in one pair.
Scope
The Venom and Pandora link is the weakest claim in this post, and I’m treating it the way I’d treat any attribution: a lead until two independent, checkable links hold it up. It names no person, and nothing in this post should be read as naming one.
Why does it sell? The reasons are sourced, and a couple are my reading.
- The victim’s machine becomes the fraud device. The browser runs on the victim’s hardware and network, so the IP address, device configuration and fingerprint match the account holder. IBM Trusteer framed hVNC in 2017 as banks’ device fingerprinting meeting its answer, F5 said the same of Dridex in 2016, Fortinet of TrickBot in 2018, and Cleafy described Gozi sessions as very hard to detect because they come from addresses the bank already knows.
- It replaced a tedious workaround. Fortinet describes the old way as renting proxies and replicating a victim’s device settings.
- It rides sessions that already passed authentication. A cloned or reused browser profile brings its cookies and saved logins. BlackFog says the hidden browser loads the victim’s existing profile, MITRE notes that stolen session cookies can bypass some multi-factor protocols, and SlashNext lists a profile cloner in Pandora’s features. The title of PureCoder’s own PureRAT thread sells the hidden desktop as a Chrome clone bypass (my evidence). “MFA already satisfied” is my wording.
- It’s site-agnostic. A web-inject has to be written per target. An operator watching a real browser can work any site. That is my reading, with Cleafy’s Gozi write-up as partial support.
- It looks like remote support. It uses documented Windows features and ordinary capture and input calls. BlackFog lists the same calls screenshot tools and remote-access software use, and there’s no exploit to patch.
- Leaks and open source seeded generations. Zeus, Gozi, Carberp, TinyNuke, Quasar, AsyncRAT and Xeno RAT, each followed by a crop of copies.
- Packaging as a service lowered the skill needed. Operator panels, marketplace listings and Telegram channels (BlackFog), seller advice on crypters (SlashNext), licensing and advertising domains (Proofpoint on VenomRAT).
- Takedowns hit sellers, not the technique. Operation Endgame disrupted VenomRAT in November 2025, and a new hVNC-first service, MedusaHVNC, was documented eight months later. No source measures the effect of the takedown on hVNC use.
One open question, and it’s an idea, not a finding. Chrome is building Device Bound Session Credentials, which tie a session to a key on the device to blunt cookie theft, and its documentation says it doesn’t protect a session registered while malware is already present. If browsers keep hardening against cookies stolen off the device, tools that act inside the browser on the device keep working by design. No source I read says demand has shifted to hVNC. A seller’s adverts and customer questions would show it.
8. The suite’s problems
Mostly marketing and detection, not leaks. eSentire found the “fully undetected” claim backed by avcheck, where crypted samples showed no detections, while at least 20 antivirus and EDR products caught them on VirusTotal. derp.ca saw PureCrypter loader builds at 41 to 49 of 76 detections in 2026, and RussianPanda found several advertised PureLogs features didn’t work in 2023.
Windows 11 24H2 broke classic process hollowing, which hasherezade documented in January 2025, and eSentire says PureCrypter was patched that month to keep its RunPE mode working. The supply chain took hits too. avcheck and three crypter sites were seized on 27 May 2025, 19 days after eSentire’s report showed the Pure bot’s scan results leaned on it, and Sellix was among the sites seized in Operation Talent in January 2025, although by then the seller had already moved to a bot. No takedown notice names PureCoder, and nobody has documented how the seller reacted.
The names are a mess (section 4), and detection content is thin. I found no PureRAT-specific YARA, Sigma or Suricata rule in any vendor report. The public network coverage is two Emerging Threats rules and some abuse.ch certificate listings (section 11).
What I couldn’t find is the trouble that dogs other commodity builders: no public report of a cracked, leaked or backdoored Pure builder, a panel vulnerability, or a dispute. For contrast, CloudSEK found a trojanized XWorm builder, passed around as a free copy, that backdoored 18,459 devices. The absence is weak evidence, because my search ran out of budget.
And on market position, the feeds disagree. On ANY.RUN’s seven-day tracker (read on 8 October 2026) PureLogs had 5 sandbox tasks and PureCrypter 2, against Remcos 281, XWorm 238 and AsyncRAT 197. In ThreatFox’s indicator feed PureRAT is second only to Cobalt Strike among named families. One counts what researchers submit to a sandbox and the other counts command servers someone reported. Neither counts victims.
9. PureMiner and the money
PureMiner is the silent miner on the 2022 list at $99: Cyble describes idle detection, running from memory, a bot killer, startup persistence and support for a long list of coins, ETHW, ETC, XMR, ERGO, BTC, RVN, KASPA and FLUX among them. Fortinet saw CountLoader push it in a Ukrainian police-impersonation campaign in 2025, and Elastic’s REF1695 report has PureMiner 7.0.6 and 7.0.7 in a fake-installer operation that also earned cost-per-action fraud commissions. Four wallets Elastic tracked had mined more than 27.88 XMR. That’s a customer’s profit, not the seller’s.
A claim I’m working from is that PureMiner and the seller’s start-up funds are connected. No public report links them. The only “startup” in public text is a persistence option on the 2022 PureMiner and PureHVNC feature lists. If the claim is real it lives in a forum or Telegram post that no vendor has quoted.
10. Who is behind it
What’s public is one finding. Check Point found GitHub URLs hard-coded in the PureRAT builder, for the plugin support files, and traced them to two accounts tied to the developer. One was named PURE-CODER-1 before a rename, the other is a test account that mirrors the same files. The commits are authored “PureCoder” and every commit Check Point examined carries a UTC+0300 time offset. Check Point notes that fits several countries, Russia among them. The builder panel comes in English, Russian and Chinese. Sekoia alone places the seller on Russian-speaking forums (XSS, UfoLabs and CrackedIO) under “PureCoder (aka PureTeam)”.
My weak reading of that offset, which is inference: the commits date from March, late October and April, and if the offset is genuine the zone is UTC+3 all year, with no summer-time shift. But the commits are web uploads, where the offset comes from the uploader’s own clock, which is trivial to set, and three timestamps don’t make a working-hours pattern. The panel’s languages describe the intended buyers, not the author’s mother tongue. And whether it’s one person or a team is unresolved: Sekoia’s alias has “Team” in it, the Telegram channels are plural, and most vendors write of a single developer.
Scope
No vendor, journalist, court or law-enforcement document I could find names a real person behind PureCoder, and neither does this post. Everything here is about a persona, a seller with products, prices and mistakes. A name would need at least two hard, checkable links, such as a shared key, wallet, email or infrastructure, or a public source that has already made the connection. Time zone, writing style and product overlap are soft signals and can’t carry a name.
11. Recognising it
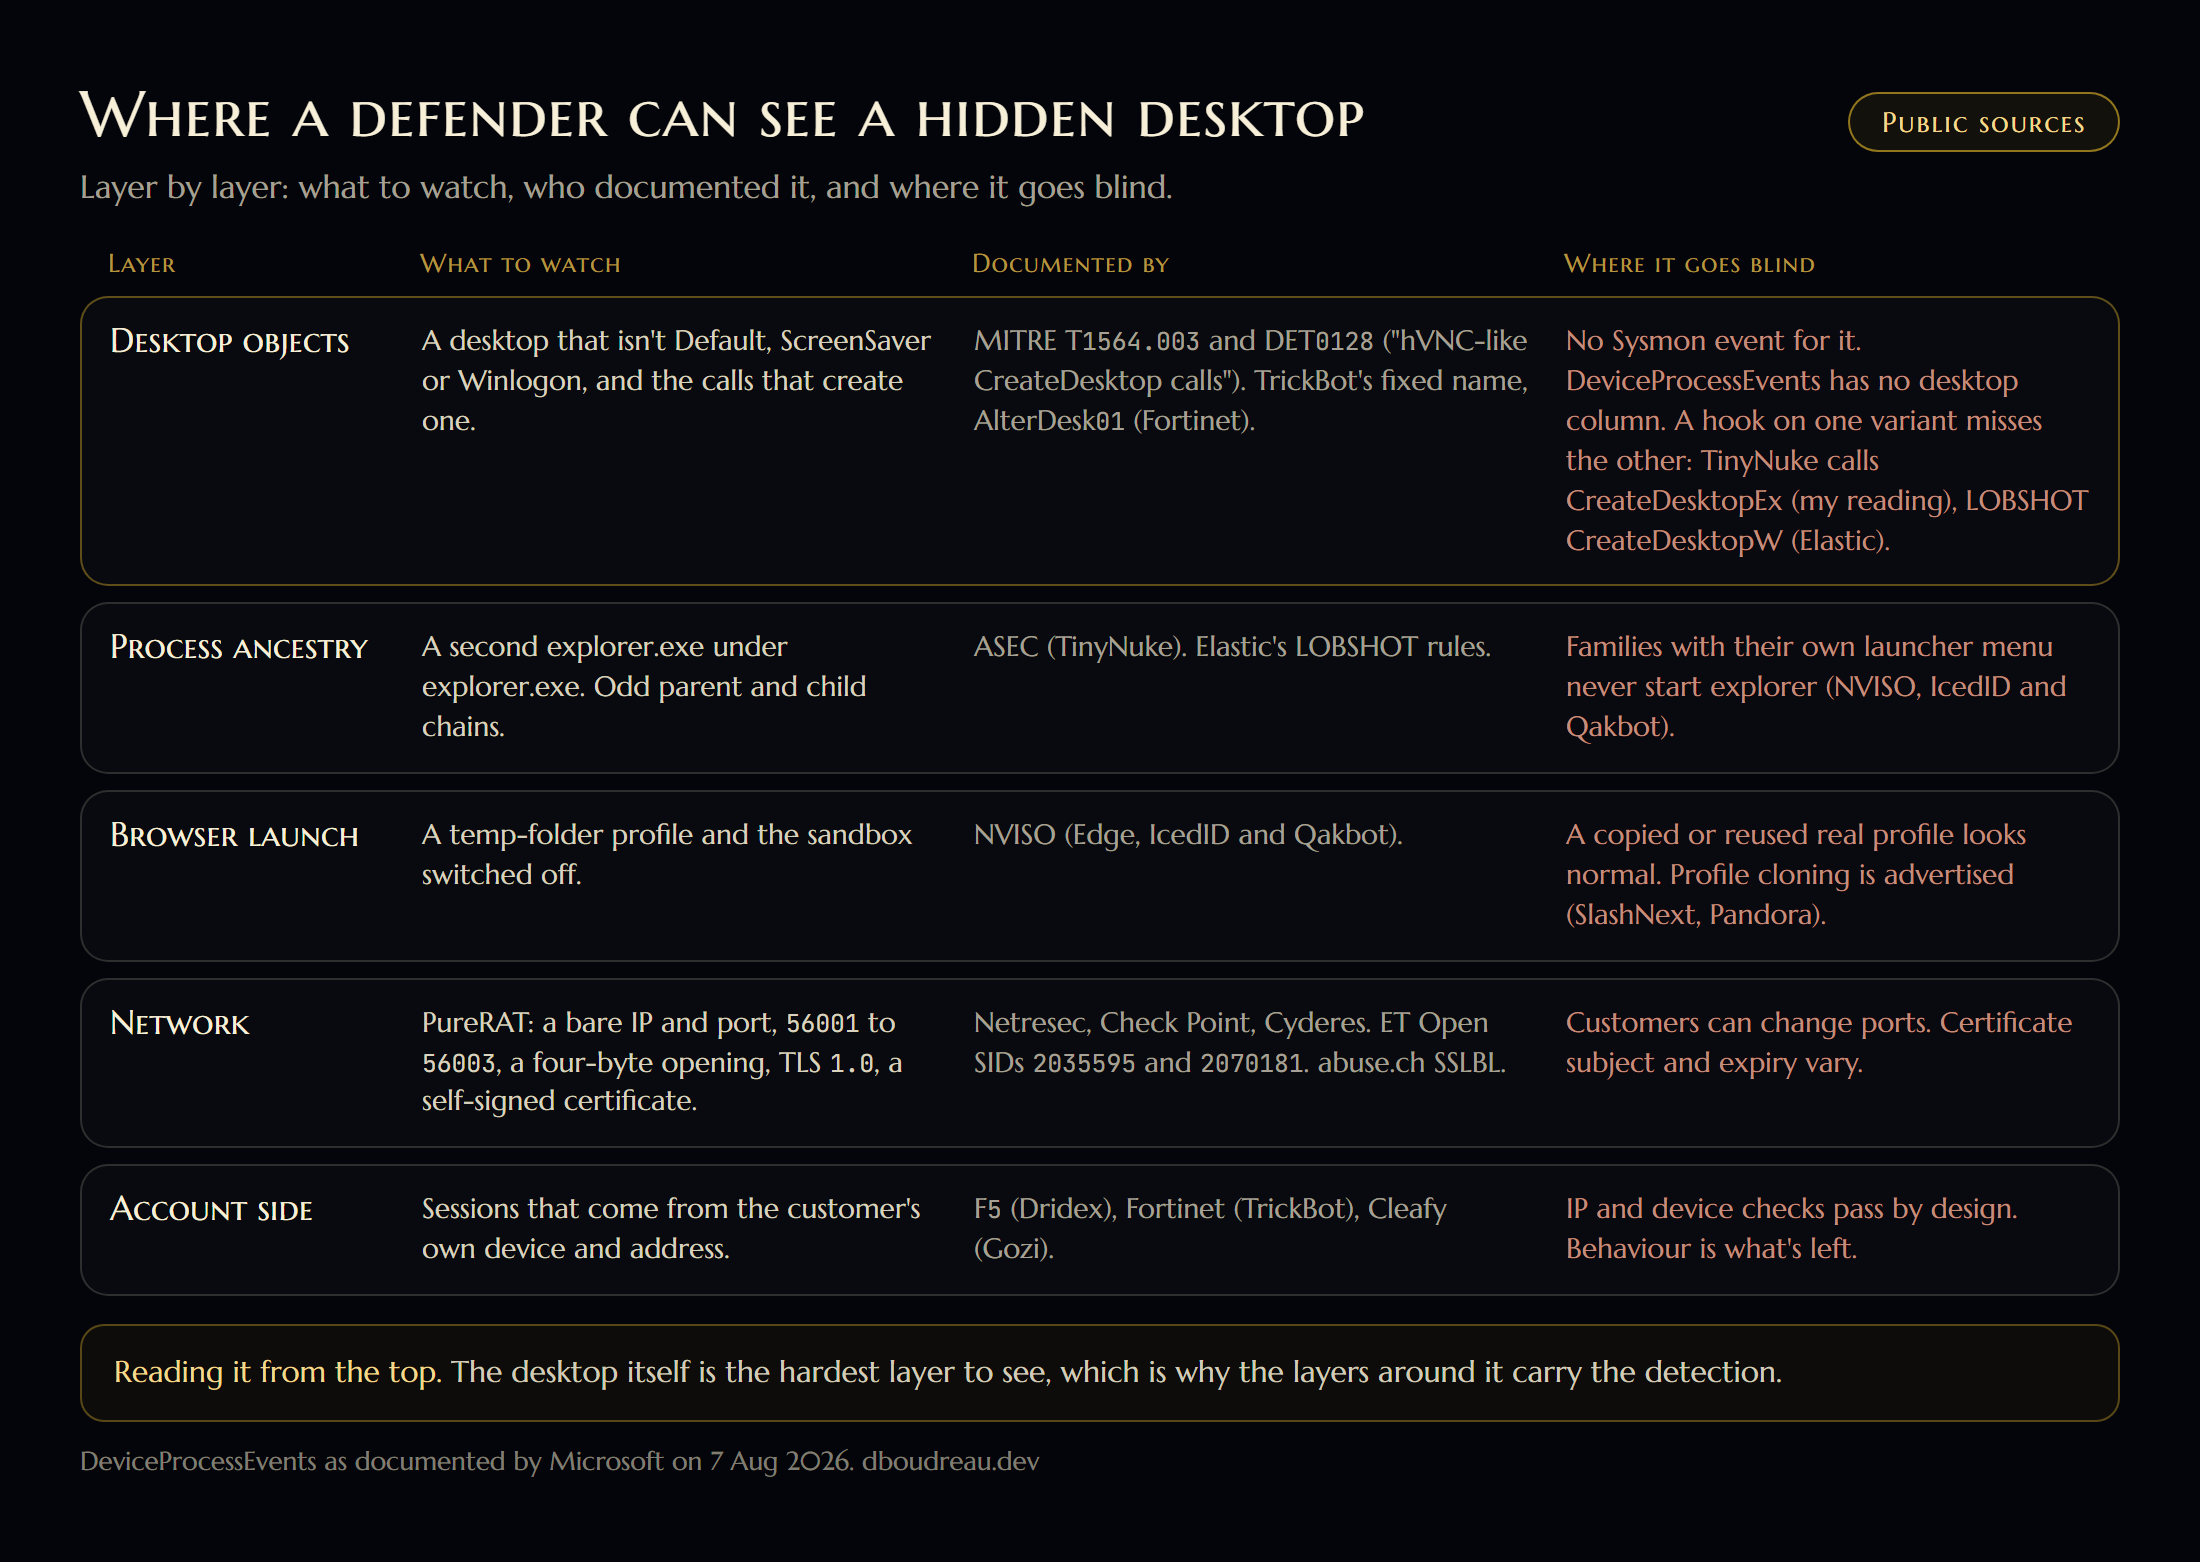
Start with what’s stable. On the network, PureRAT defaults to a bare IP and port, 56001 to 56003, a four-byte opening, an old-style TLS handshake and a self-signed certificate with a subject of “PureRAT Agent” or random letters. On the host, older builds leave a registry key named with 32 hex characters under HKCU\Software holding large blobs, a scheduled task repeating every five minutes with an encoded PowerShell action and an updater-style name, and .NET utilities (RegAsm, AddInProcess32, InstallUtil, msbuild, jsc, AppLaunch, csc, SearchUI) hosting the payload and making network connections. Huntress and Cyderes both saw AMSI and ETW patching.
For the hidden desktop itself, MITRE’s detection strategy for T1564.003 (DET0128) tells you to correlate hVNC-like desktop creation with odd process lineage. In practice that means a second explorer.exe under explorer.exe (ASEC on TinyNuke, Elastic on LOBSHOT), and browsers started with a profile in the temp folder and the sandbox switched off (NVISO). Each of those goes blind somewhere. Families with their own launcher menu never start explorer, a copied real profile looks normal, and I found no public Sysmon event or default ETW provider for desktop creation. A hook on one create call also misses the other: TinyNuke makes its desktop with CreateDesktopEx on my reading, and LOBSHOT with CreateDesktopW on Elastic’s.
Recommendations at base level
- Alert on a second
explorer.exeunderexplorer.exe, and on browsers started with a temp-folder profile and the sandbox off. - Log desktop creation where your EDR can, and cover every variant of the call, the plain ones and
CreateDesktopEx, in ANSI and Unicode. Test that your sensor sees them on your builds. - Watch egress for bare IPs on ports 56001 to 56003, TLS to an address with a self-signed certificate, and the two Emerging Threats rules below. Ports are the customer’s choice, so don’t stop at the defaults.
- Hunt the registry for
HKCU\Softwarekeys named with 32 hex characters that hold large binary values. - Treat .NET utilities that make network connections as suspicious, especially RegAsm, AddInProcess32 and InstallUtil started from user-writable folders.
- Protect the account side. A session driven from the customer’s own device passes IP and device checks by design, so use short sessions, step-up on risky actions and behaviour analytics, and use device-bound session credentials where your browsers support them.
Public rules exist, and they’re thin. I haven’t run any of them against samples, so test them on your own corpus before you trust a miss.
| Source | Rule | What it covers |
|---|---|---|
| Emerging Threats Open | SID 2035595, retitled “ET MALWARE PureRAT SSL Cert” on 29 Sep 2026 | A broad certificate match. It began as a generic AsyncRAT and zgRAT rule and still fires on AsyncRAT |
| Emerging Threats Open | SID 2070181 (named by Netresec) | PureRAT traffic. I haven’t read the rule text |
| abuse.ch SSLBL | PureRAT certificate listings | Certificate fingerprints, which move when the builder changes its subject or dates |
| ditekSHen, in public YARA sets | MALWARE_Win_zgRAT | Don’t use it as family evidence. It matches any .NET Reactor binary |
| Elastic | “Suspicious Windows Explorer Execution” and “Suspicious Parent-Child Relationship” | Hidden-desktop behaviour in the LOBSHOT report, not PureRAT itself |
| Wazuh | Rules 100201 to 100207 | The Fortinet PureHVNC chain, not the RAT |
| MITRE ATT&CK | DET0128, hidden windows | A detection strategy, with hVNC-like desktop creation and lineage as its core |
12. What I’d do next
- Get the hidden-VNC plugin itself: from a live session, or a sandbox run where the C2 pushed it. Then record which create call it makes (the plain one or
CreateDesktopEx), the desktop name, how processes are placed on the desktop, the capture and input calls, how the browser profile is handled, and whether it opens its own socket or rides the RAT’s TLS channel. - Compare that against the TinyNuke-derived
hvnccode in the leaked BitRAT client, and look for the AVE_MARIA and LIGHT’s BOMB markers. A match makes PureHVNC part of the TinyNuke line. A mismatch rules out a paste, not a rewrite. - Follow the PureHVNC project that was sold in December 2021: who bought it, and whether a later seller’s hVNC shares its reflective loader.
- Settle the version puzzle (0.3.9, 3.0.1, 4.1.9, 4.4.2) and Elastic’s no-TLS PureRAT, from the seller’s own changelog if someone has it. Test whether a sample’s file version decodes to a build date.
- Find out what replaced avcheck in the bot’s scan results after the seizure, and whether the GitHub finding changed anything.
Mapping the personas behind these families, and the infrastructure that links them, is graph work. I do mine in NocTORnal, the social network analysis software I write, on GitHub. The family indicators behind the opening figure are on the Threat orrery.
Operation Endgame’s line: “Think about (y)our next move.” https://operation-endgame.com
References
- Check Point Research, Under the Pure Curtain: From RAT to Builder to Coder (16 Sep 2025).
- eSentire TRU, Ghost Crypt Powers PureRAT with Hypnosis (17 Jul 2025), and Pure Crypter Malware Analysis: 99 Problems but Detection Ain’t One (8 May 2025).
- Netresec, PureRAT = ResolverRAT = PureHVNC (12 Aug 2025), and PureLogs, PureRAT and misleading zgRAT (27 Jul 2026, updated 5 Oct 2026).
- Emerging Threats community forum, False positive 2035595: zgRAT / PureRAT confusion (22 Jul to 5 Oct 2026).
- Cyble, Pure coder offers multiple malware for sale in darkweb forums (27 Dec 2022), and Fileless Pure Clipper malware (18 Oct 2023).
- ANY.RUN, A Full Analysis of the Pure Malware Family (16 Jan 2024).
- Zscaler ThreatLabz, Technical Analysis of PureCrypter (13 Jun 2022). Menlo Security, PureCrypter Targets Government Entities Through Discord (21 Feb 2023).
- Fortinet FortiGuard Labs, PureHVNC Deployed via Python Multi-stage Loader (8 Aug 2024).
- Huntress, A Vietnamese threat actor’s shift from PXA Stealer to PureRAT (25 Sep 2025). Symantec and Carbon Black, PureRAT: Attacker Now Using AI to Build Toolset (28 Jan 2026). Cyderes, Inside Two Multi-Stage Attack Chains Hiding Behind Job Offers (10 Sep 2026).
- The Hacker News, PureRAT Malware Spikes 4x in 2025, on Kaspersky (21 May 2025).
- Flashpoint, PureLogs: low-cost infostealer, high-impact threat (10 Oct 2024).
- Elastic Security Labs, Fake Installers to Monero: A Multi-Tool Mining Operation (31 Mar 2026), and Elastic Security Labs discovers LOBSHOT malware (16 May 2023).
- AhnLab ASEC, VNC Malware (TinyNuke, TightVNC) Used by Kimsuky Group (27 Sep 2021). NETSCOUT ASERT, Dismantling Nuclear Bot (19 Dec 2016). Security Affairs, Nuclear Bot source code leaked online, on IBM X-Force (30 Mar 2017).
- dboudreau.dev, my analysis of the leaked BitRAT client source (12 Sep 2022), and PandorahVNC (28 Jul 2021).
- Microsoft Learn, Desktops and CreateDesktopExW. MITRE ATT&CK, T1564.003 Hidden Window and DET0128.
- Krebs on Security, SpyEye vs. ZeuS Rivalry, on SecureWorks (1 Apr 2010). F5 Labs, Dridex is watching you (17 Jun 2016). Fortinet, I’ve Got Trickbot Under My Screen (23 May 2018).
- NVISO Labs, IcedID and Qakbot’s VNC Backdoors: Dark Cat, Anubis and Keyhole (20 Mar 2023). BlackFog, MedusaHVNC: A Hidden Desktop (27 Jul 2026).
- SlashNext, Pandora hVNC (13 Dec 2023). Intrinsec, A stalker in the box (26 Sep 2024). Cyfirma, via The Hacker News, Open-Source Xeno RAT Trojan (27 Feb 2024).
- ESET, Unmasking AsyncRAT: Navigating the labyrinth of forks (15 Jul 2025). SonicWall, AsyncRAT is now going fileless (21 Jul 2022). Censys, AsyncRAT C2 Activity at Internet Scale (29 Jan 2026).
- CloudSEK, What Is The Venom RAT? (19 Nov 2021). Proofpoint, VenomRAT Defanged (13 Nov 2025). CyberScoop, Operation Endgame disrupts global malware networks (13 Nov 2025).
- derp.ca, PureLogs: Reverse Engineering a .NET RAT From the PureCoder Ecosystem (updated 26 Feb 2026).
- hasherezade, Process Hollowing on Windows 11 24H2 (27 Jan 2025). Politie, Key service for malware developers taken offline (30 May 2025). The Hacker News, U.S. DoJ Seizes 4 Domains Supporting Cybercrime Crypting Services (27 May 2025).
- BleepingComputer, hacker infects 18,000 script kiddies with fake malware builder, on CloudSEK (24 Jan 2025).
- Cleafy, Digital banking fraud: how the Gozi malware works (25 Oct 2021). Chrome for Developers, Device Bound Session Credentials.
- abuse.ch, ThreatFox, the source of the 48-hour indicator counts.